Author: wpx_

  • RDP Port: TCP 3389, UDP, Configuration, and Security

    RDP Port: TCP 3389, UDP, Configuration, and Security

    You reach a Windows desktop or server over Remote Desktop Protocol (RDP), and that connection lands on one well-known listener unless someone changed it. Remote Desktop listens on TCP port 3389 by default, and modern Windows versions also use UDP port 3389 for faster session traffic; an RD Gateway moves the public side of the connection to TCP 443 and UDP 3391. Knowing which port is in play on your host tells you what to open, what to test, and what to lock down.

    A laptop and desktop computer connected in an office.

    The same number that makes remote desktop easy to reach also makes it easy to find. Port 3389 is one of the most scanned ports on the internet, and an exposed listener draws brute-force attempts within hours of going live.

    At PacketTools, the guidance below comes from the same checks used on production networks: confirming the rdp port a host listens on, proving reachability from the outside, changing the listener without locking yourself out, and keeping access restricted once it works.

    Which Ports Does Remote Desktop Use by Default?

    A desktop computer connected to a network switch with one port illuminated.

    A standard Windows or Windows Server host accepts Remote Desktop Protocol connections on port 3389 over both TCP and UDP. TCP carries the session setup and acts as the guaranteed path, while UDP speeds up graphics and input when the network allows it.

    Scenario Port(s) Protocol
    Direct RDP to a Windows host 3389 TCP and UDP
    RD Gateway, public side 443 / 3391 TCP / UDP
    RD Gateway to internal hosts 3389 TCP and UDP
    xrdp on Linux (default) 3389 TCP

    Why Does RDP Use TCP 3389 and UDP 3389?

    Microsoft registered 3389 for Terminal Services, and the RDP server has kept it ever since. The server listens on TCP port 3389 and UDP port 3389 out of the box.

    TCP 3389 handles the handshake: security negotiation, TLS, Network Level Authentication, and the initial session channels. Once the session is up, the RDP client and server try to add a UDP transport on the same port number. UDP avoids the retransmission stalls that hurt TCP on lossy or high-latency links, so scrolling, video, and typing feel more responsive.

    When you open firewall rules for a direct connection, allow both protocols on 3389. Microsoft lists TCP and UDP 3389 as the standard RDP port, configurable to a different number on both host and client.

    Does Remote Desktop Still Work When UDP Is Blocked?

    Yes. If UDP 3389 is filtered anywhere along the path, the session falls back to TCP only and still connects.

    You will notice the difference on poor links. Over a clean LAN, TCP-only sessions feel nearly identical. Over Wi-Fi with packet loss or a long WAN path, expect laggier screen updates. In the Remote Desktop Connection client, the connection info icon in the top bar shows whether UDP is active.

    Some VPNs behave badly with RDP over UDP, producing freezes or random disconnects. If a session over VPN keeps hanging, disabling the UDP transport on the client through Group Policy (“Turn Off UDP On Client”) is a practical test.

    Do Windows, Linux, and Other Clients Use Different Ports?

    No. The port belongs to the server, and every client connects to whatever the server listens on.

    • Windows: mstsc.exe and the Windows App default to 3389.
    • macOS and iOS: Microsoft’s Windows App also targets 3389 unless you append a port.
    • Linux clients: Remmina and FreeRDP use 3389 by default, with /v:host:port or a port field for custom values.
    • Linux servers: xrdp listens on TCP 3389 by default, set in /etc/xrdp/xrdp.ini.

    If you run xrdp and Windows hosts behind the same public address, each needs its own external port or a gateway in front.

    How Do RD Gateway and RDS Change the Connection Path?
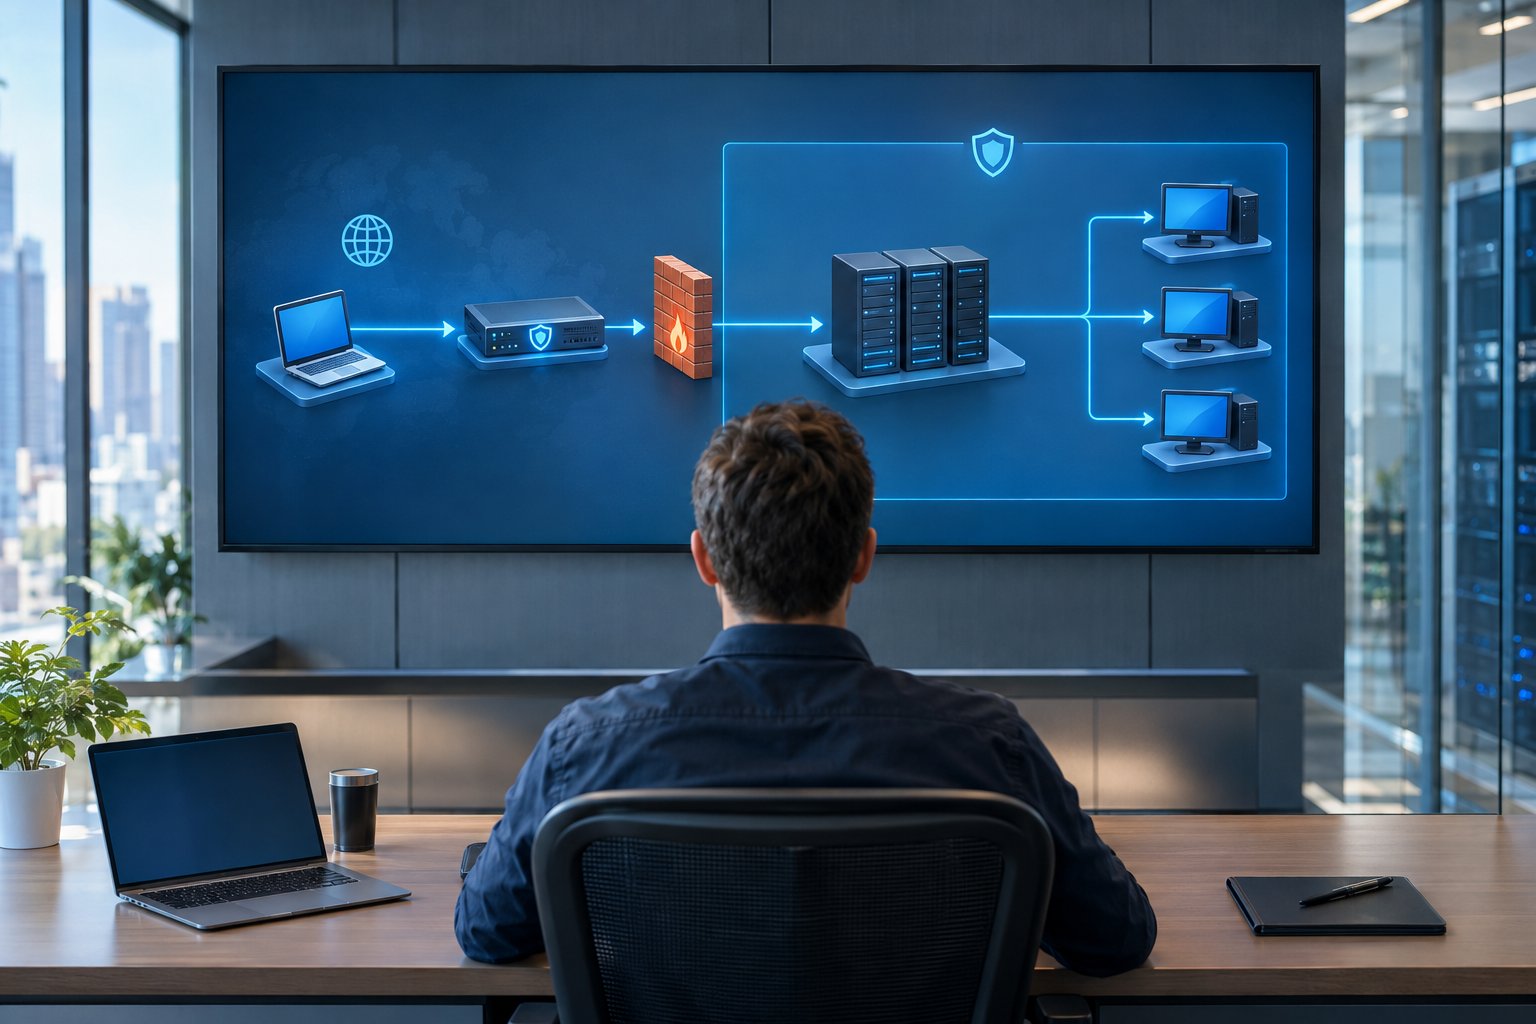
    A network administrator views a diagram of a laptop connecting through a gateway and remote desktop servers to office computers.

    RD Gateway puts an HTTPS front door in front of your hosts, so the internet sees TCP 443 and UDP 3391 while 3389 stays internal. Full Remote Desktop Services (RDS) deployments add more roles, each with its own internal ports for brokering, web feeds, and licensing.

    When Does RD Gateway Use TCP 443 and UDP 3391?

    Every gateway connection starts on TCP 443. Clients reach the gateway over TCP 443 for HTTP over SSL and UDP 3391 for RDP over UDP, and both ports can be changed in RD Gateway Manager.

    The gateway then talks to internal hosts on TCP and UDP 3389. Your perimeter firewall only needs 443 (plus optional 3391) pointed at the gateway, and 3389 never faces the internet.

    Certificates make or break this setup. The gateway first establishes an encrypted SSL tunnel using a certificate the client recognizes, then authenticates the user and can use RADIUS for multi-factor authentication. Use a publicly trusted certificate in production, or every client needs your private chain installed.

    If UDP 3391 is blocked, sessions still work over 443 at reduced responsiveness, mirroring the direct-connection fallback.

    How Do RD Web Access and RemoteApp Fit In?

    RD Web Access publishes desktops and RemoteApp programs as a feed over HTTPS on TCP 443. Users sign in to the web portal or subscribe from the Windows App, then launch resources that open through the gateway.

    RemoteApp uses the same RDP channel as a full desktop; only the presentation differs, with a single application window on the user’s screen. From a firewall view, a RemoteApp launch generates identical traffic to a desktop session: 443 to the gateway, then 3389 internally.

    Internally, RD Web Access reaches the Connection Broker on TCP 5504 for centralized publishing.

    Which Additional Ports Are Specific to RDS Roles?

    Internal role-to-role traffic is where segmented networks break RDS. The common ones:

    • Connection Broker: TCP 5504 to RD Web Access, TCP 3389 to session hosts, TCP 445 plus RPC to session and virtualization hosts.
    • RD Gateway internal: TCP 88 (Kerberos), TCP 135 (RPC Endpoint Mapper), TCP/UDP 389 (LDAP), TCP/UDP 53 (DNS), UDP 1812 and 1813 when NPS handles RADIUS.
    • RDS Licensing: TCP 135 plus dynamic RPC on TCP 49152 to 65535 on Windows Server 2008 and later, TCP 445, and TCP 443 to the Microsoft Clearing House.
    • Administration: TCP 5985 for WMI and PowerShell Remoting across every role.

    If session hosts cannot find a license server, check RPC first. A firewall that allows 135 but blocks the dynamic range produces exactly that symptom.

    How Can You Check the Listener and Troubleshoot Connectivity?

    Start on the host to confirm what it listens on, then test from the client side to prove the path is open. Splitting the problem this way tells you whether to look at the server, the network, or the credentials.

    Find the Configured Listening Port With PowerShell and netstat

    The configured port lives in the registry. In an elevated PowerShell window, run:

    Get-ItemProperty -Path 'HKLM:SYSTEMCurrentControlSetControlTerminal ServerWinStationsRDP-Tcp' -Name PortNumber

    That shows the configured value. To confirm the service is bound to it, check live sockets:

    netstat -ano | findstr ":3389"

    Look for a LISTENING line on 0.0.0.0:3389 and [::]:3389. Match the PID against TermService with tasklist /svc /fi "PID eq <pid>".

    If nothing listens, run qwinsta. Microsoft’s guidance says that if the list shows rdp-tcp with a status of Listen, the listener works. Also confirm TermService and UmRdpService are running, and that a GPO is not setting fDenyTSConnections to 1.

    Test TCP Reachability With Test-NetConnection

    From the client, run:

    Test-NetConnection server01.corp.local -Port 3389

    TcpTestSucceeded : True proves a TCP handshake completed from that machine to that port. It says nothing about UDP, credentials, or whether a session will start.

    When the result is False, the output still helps. A PingSucceeded of True with a failed TCP test points at a firewall or a stopped listener. A failed name resolution line points at DNS. For testing from outside your network, the PacketTools open port checker shows whether 3389 or your custom port is reachable from the public internet, which is often the very exposure you want to rule out.

    Separate DNS, Routing, Firewall, and Sign-In Failures

    Work through the stages in order and repeat the same test after each change:

    1. DNS: Does the name resolve to the right IP? Compare Resolve-DnsName output against the host’s real address. Stale records after a migration are common.
    2. Routing: Can you reach the subnet? Traceroute shows where packets stop.
    3. Firewall: Check Windows Firewall rules for “Remote Desktop – User Mode (TCP-In)” on the active profile, then any perimeter, NSG, or VPN filter.
    4. Listener: Confirmed with netstat and qwinsta above.
    5. Sign-in: If the port answers but you get credential or NLA errors, the network is fine. Check group membership in Remote Desktop Users, account lockout, and certificate warnings.

    That staged approach is the core of solid network troubleshooting: each test isolates one layer before you touch configuration.

    How Do You Change the Listening Port Without Losing Access?

    Change the registry value, open the new port in every firewall, and only then restart Remote Desktop Services. Getting that order wrong on a remote host is the classic way to cut off your own session.

    Choose an Unused Port and Prepare a Recovery Path

    Pick a port in the registered range (1024 to 49151) and stay away from well-known ports below 1024. Confirm nothing else uses it:

    netstat -ano | findstr ":3390"

    An empty result means it is free. Avoid ports your other applications may claim later, and document the choice.

    Before touching anything, line up a second way in: a hypervisor or cloud serial console, iLO/iDRAC, or a working PowerShell Remoting session on TCP 5985. On a VPS with only RDP access, this step is the difference between a two-minute fix and a support ticket.

    Update PortNumber With PowerShell or Registry Editor

    With PowerShell as administrator:

    Set-ItemProperty -Path 'HKLM:SYSTEMCurrentControlSetControlTerminal ServerWinStationsRDP-Tcp' -Name PortNumber -Value 3390

    In Registry Editor, browse to the same RDP-Tcp key, open the PortNumber DWORD, select Decimal, and enter the new value. Entering it while Hexadecimal is selected is a frequent mistake that produces a completely different port.

    The change does nothing until TermService restarts. The custom RDP port applies to both TCP and the UDP port used for the faster transport.

    Scope Firewall Rules Before Restarting Remote Desktop Services

    Microsoft’s procedure adds inbound TCP and UDP rules for the new port with New-NetFirewallRule. Add a source restriction so the rule admits only your management networks:

    New-NetFirewallRule -DisplayName 'RDP-3390-TCP' -Direction Inbound -Protocol TCP -LocalPort 3390 -RemoteAddress 10.20.0.0/24 -Action Allow
    New-NetFirewallRule -DisplayName 'RDP-3390-UDP' -Direction Inbound -Protocol UDP -LocalPort 3390 -RemoteAddress 10.20.0.0/24 -Action Allow

    Update any cloud security group, router NAT, or perimeter firewall too. Then restart the service:

    Restart-Service TermService -Force

    Your current session drops at this point. That is expected.

    Connect With mstsc.exe and Verify the New Port

    Reconnect with the port appended: mstsc.exe /v:server01:3390, or type server01:3390 in the Remote Desktop Connection address box.

    Confirm the result from both sides. On the host, netstat -ano | findstr ":3390" should show LISTENING. From the client, Test-NetConnection server01 -Port 3389 should now fail and port 3390 should succeed. Once confirmed, disable the old built-in Remote Desktop rules so 3389 is not left open by accident.

    How Do You Secure Remote Access Beyond Changing the Port?

    A new port number cuts scanner noise, but malicious bots fingerprint RDP on any port within minutes. Real RDP security comes from limiting who can reach the listener at all, then hardening authentication for those who can.

    Keep Public RDP Behind a VPN or Hardened RD Gateway

    Never publish rdp port 3389, or any custom port, directly to the internet. Exposed RDP remains a leading entry point for ransomware operators, who buy stolen credentials and spray them at open listeners.

    Your realistic options:

    • VPN: Users connect to the network first; RDP is reachable only from VPN address pools.
    • RD Gateway: One hardened HTTPS endpoint with RD CAPs and RD RAPs controlling who reaches which host, plus MFA through NPS and RADIUS.
    • SSH tunnel: Workable for a few admins: forward a local port to the host’s 3389 over an SSH bastion.

    Patch the gateway or VPN appliance aggressively. It becomes the exposed surface in place of every individual host.

    Require NLA, Validate TLS, and Enforce Strong Authentication

    Network Level Authentication (NLA) forces users to authenticate before the server builds a session, which blocks unauthenticated attackers from consuming resources or reaching pre-auth bugs. Enable it in System Properties or via Group Policy under Remote Desktop Session Host > Security.

    Replace the self-signed certificate with one from your internal CA or a public CA, and set the security layer to TLS. Users who learn to click through certificate warnings will click through a spoofed one too.

    Pair this with MFA at the gateway or VPN, an account lockout policy, and Windows LAPS so local administrator passwords differ on every machine.

    Use Group Policy, Restricted Firewall Rules, and Access Monitoring

    Group Policy keeps these settings consistent across hundreds of hosts: NLA required, TLS security layer, session timeouts, and Remote Desktop Users limited to specific groups.

    Scope firewall rules by source address everywhere, including inside the LAN, so workstations cannot RDP laterally to servers. Jump hosts or privileged access workstations make good sole sources.

    Watch the logs. Event ID 4625 with logon type 10 or 3 flags failed RDP sign-ins, and 4624 type 10 shows successful ones. A spike from one IP or many accounts is brute forcing; forward these events to your SIEM and alert on them.

    Verify the Connection Path and Keep RDP Access Restricted

    RDP listens on TCP and UDP 3389 by default, with TCP as the guaranteed path and UDP as the performance layer. RD Gateway shifts the public side to TCP 443 and UDP 3391 while 3389 stays internal.

    Confirm the listener with the registry, netstat, and qwinsta, then prove reachability with Test-NetConnection and an external port check. If you move to a custom port, set firewall rules before restarting TermService and keep a console path ready.

    Treat the port number as a minor detail. Put access behind a VPN or gateway, require NLA and TLS, scope firewall rules to known source addresses, and alert on failed logon events.

  • TP-Link Default Password: Find Your Login and Restore Access

    TP-Link Default Password: Find Your Login and Restore Access

    Your TP-Link router has two credentials that are easy to confuse. One is the admin password, which opens the router’s settings page. The other is the Wi-Fi password, which lets your devices join the network. Mixing them up is the most common reason a login attempt fails.

    A person configures a wireless router beside a laptop.

    For the tp link default password, older TP-Link routers use “admin” as both the username and password. Newer models have no default login and ask you to create your own admin password the first time you sign in. Your default Wi-Fi name and key are printed on the label on the router. If the admin password you set is lost, recovery depends on what you configured ahead of time. Without a recovery option, you need a factory reset.

    At PacketTools, we troubleshoot this kind of access problem in production networks all the time. Below, you can work out which credential applies to you, reach the login page, and try every recovery path before you wipe your configuration.

    Which Credentials Does Your Router Actually Use?

    A person checks the label on a home Wi-Fi router beside a laptop.

    Your router’s age, your firmware, and whether you linked a TP-Link ID together decide what the login screen accepts. Some routers from internet service providers add their own credentials on top of these.

    Older Models May Use admin/admin; Newer Models Require Your Own Password

    Older TP-Link routers ship with admin as the username and admin as the password. On these models, the login form shows two fields, and sometimes both are pre-filled.

    Newer models have no shared default. TP-Link confirms that newer router models require you to create a custom admin password on first login, while older ones keep “admin” for both fields. If your login screen shows a single password box with no username field, you have the newer style. In that case, typing “admin” will not work unless you chose it yourself.

    A quick way to tell which type you have:

    Login screen shows Likely model type What to enter
    Username + password fields Older admin / admin (unless changed)
    Single password field Newer The password you created
    “Create password” prompt New or freshly reset Choose a new password
    TP-Link ID toggle Cloud-linked Your TP-Link ID email and password

    How Do Admin, Wi-Fi, and TP-Link ID Passwords Differ?

    Three separate passwords can exist on one router:

    • Admin (local management) password: opens the web interface at tplinkwifi.net or the router’s IP address.
    • Wi-Fi password (wireless key): joins your devices to the network identified by its SSID.
    • TP-Link ID password: your cloud account, used by the Tether and Deco apps and for remote management.

    TP-Link support staff stress that the password requested on first access is the router’s management password, not your TP-Link ID password and not your Wi-Fi password. One detail catches people out. Once a cloud router is bound to a TP-Link ID, the local login password you created becomes ineffective, and you sign in with the TP-Link ID instead.

    A useful test: if your phone still connects to Wi-Fi but the admin page rejects you, your problem is the admin password. If you cannot join the network at all, the problem is the wireless key.

    Where Can You Find Model-Specific or ISP Login Details?

    Check the router itself first. Default credentials sit on a label on the back or bottom of the device under headings such as Default Access, Default Settings, or Default Wireless Access. The same details appear in the Quick Installation Guide that came in the box.

    Routers supplied by your internet provider are different. ISPs often ship TP-Link hardware with custom firmware, a different login address, or an account-specific password. If your label carries the ISP’s logo or lacks a “Default Access” block, the provider’s support documentation or help line holds the correct details. Some ISP units also lock certain settings no matter which password you use.

    How Do You Open the Router’s Login Page?

    A person uses a laptop beside a Wi-Fi router.

    Connect to the router, then type tplinkwifi.net or its local IP into the address bar. If neither address loads, look up the default gateway your computer received and use that.

    Connect to the Router by Ethernet or Wi-Fi

    The management page runs on the router itself, so it works without internet service. Your device does need to be on the router’s own network.

    • Ethernet: plug into one of the yellow LAN ports, not the WAN/internet port. Confirm the matching LAN LED lights up.
    • Wi-Fi: join the router’s SSID. On a fresh or reset unit, use the network name and key from the label.

    A wired connection is the safer choice when you plan to change wireless settings. If you edit the SSID or password over Wi-Fi, your session drops the moment you save.

    Open tplinkwifi.net or the Router’s Local IP Address

    Use Chrome, Firefox, or Edge, and type one of these directly into the address bar:

    1. tplinkwifi.net
    2. 192.168.0.1
    3. 192.168.1.1 (common on older and ISP models)

    If you type the address into a search box, you get search results and never reach the login page. The tplinkwifi.net name only resolves while you are connected to a TP-Link router. On a mesh system or a MiFi hotspot, the hostname differs, and the label lists the right one.

    Find the Actual Gateway Address When the Defaults Fail

    If someone changed the LAN subnet, neither default address works. Your computer already knows the real one, listed as the default gateway:

    • Windows: run ipconfig and read “Default Gateway.”
    • macOS: run route -n get default | grep gateway, or check System Settings > Network > Details > TCP/IP.
    • Linux: run ip route | grep default.
    • iPhone/Android: open the connected Wi-Fi network’s details and look for “Router” or “Gateway.”

    Type that address into the browser. If you want to know more about how gateways are assigned, our guide to your router IP address covers the private ranges routers use and why some units hand out 10.x or 172.16.x addresses.

    Where Can You Find or Change the Wi-Fi Password?

    The router label holds the factory Wi-Fi key, and the wireless settings page shows whatever key is set now. MiFi hotspots use their own login address and app.

    Check the Label for the Original Network Name and Wireless Key

    On most TP-Link routers, the label lists the default SSID and wireless password. On many models, the default SSID is TP-Link_XXXX and is case-sensitive, with the last characters drawn from the MAC address.

    The label only helps if nobody changed the settings. If the network name broadcasting near you differs from the label, the key has almost certainly changed too. Dual-band routers often list a separate “_5G” SSID that uses the same key.

    View or Update the Password in Wireless Settings

    After you log in to the admin page, the menu path depends on firmware. TP-Link lists Wireless > Wireless Settings or Basic > Wireless as the usual locations. Some older models split the SSID onto Basic Settings and the key onto Wireless Security.

    To change it:

    1. Open the wireless page and select the password field (some firmware hides it behind an eye icon).
    2. Enter a new key of at least 12 characters, mixing letters, numbers, and symbols.
    3. Use WPA2-PSK or WPA2/WPA3 mixed mode if your devices support it.
    4. Save, then reconnect each device with the new key.

    On dual-band routers, check whether each band has its own key field.

    Find Mobile Wi-Fi Details Using tplinkmifi.net or the tpMiFi App

    TP-Link’s portable M-series hotspots use tplinkmifi.net in place of tplinkwifi.net. Connect to the hotspot, open that address, and the wireless menu shows the SSID and key. Many units print the default key under the battery cover, and some show it on their screen.

    The tpMiFi app for iOS and Android does the same job from your phone. Once connected, it shows the network name and password, along with battery level and data usage.

    What Should You Check When the Login Page Will Not Load?

    Most failures come down to your device sitting on the wrong network or subnet, or to something on your device blocking local traffic. Work from the network layer up before you suspect the router.

    Check Local Addressing and Test Gateway Reachability

    Your device needs an address from the router’s DHCP pool. Run ipconfig or ip addr and compare it with the gateway:

    • 192.168.0.x pairs with gateway 192.168.0.1.
    • 192.168.1.x pairs with gateway 192.168.1.1.
    • 169.254.x.x means DHCP failed, so you have no working connection to the router.

    Next, run ping 192.168.0.1 (or your gateway). Replies mean the router is alive and the problem lies in the browser or in security software. TP-Link notes that firewall or antivirus software can block access to the router. No replies point to cabling, a wrong subnet, or a static IP set on your adapter. Our IP address basics guide explains subnets and why mismatched ranges cannot talk to each other.

    Rule Out Guest Network Isolation, VPN Routing, and Mobile Data

    Three common traps block access even when your Wi-Fi icon looks healthy:

    • Guest network: guest SSIDs block access to the admin page by design. Switch to the main network.
    • VPN or proxy: a full-tunnel VPN sends 192.168.x.x traffic down the tunnel. Disconnect it, or enable your client’s local network access option.
    • Mobile data: phones sometimes fall back to cellular when Wi-Fi has no internet. Turn off mobile data while you log in.

    Corporate laptops with always-on VPN agents are the usual culprit. Test from a personal device first.

    Troubleshoot Browser Sessions and Verify Certificate Warnings

    Stale cookies and cached redirects can leave the login page blank or stuck in a loop. Open a private window, try another browser, or clear site data for tplinkwifi.net. Disable any extensions that rewrite pages.

    A “Your connection isn’t private” warning is expected. The router uses a self-signed certificate, so click Advanced and proceed. Check that the address bar shows your actual gateway IP or tplinkwifi.net before you continue. A warning on any other hostname deserves suspicion.

    Separate Local Router Access Problems From Internet Connectivity Faults

    The admin page and your internet connection are separate paths. If the gateway answers ping but websites fail, the fault sits upstream at the WAN link, the modem, or the ISP. If the gateway does not answer, the internet is irrelevant until local access works.

    Once you are online, the PacketTools What Is My IP tool confirms your public address, and Ping Test and Traceroute show whether traffic leaves your network cleanly. These run from our servers, so they test the public side and cannot reach your private 192.168 gateway. Use your computer’s own ping for that. Our network troubleshooting guides follow this same layered order through DNS and latency.

    How Can You Recover Access Before Factory Resetting?

    Check stored credentials, any recovery feature you enabled earlier, a linked TP-Link ID, and your ISP before you reset. A reset always works, but it costs you every setting on the router.

    Check Saved Passwords and Supported Recovery Options

    Start with the places a password may already be stored:

    • Browser password storage: Chrome, Edge, Firefox, and Safari often saved the router login. Search for “192.168” or “tplinkwifi.”
    • Password manager: search your vault for the router model or “admin.”
    • Setup notes: check the Quick Installation Guide card, a photo of the label, or IT documentation.
    • Logged-in devices: a tablet or the Tether app may still hold an active session.

    Then look for Forgot Password? on the login page. It works only if you set up recovery beforehand. TP-Link’s feature supports recovery by email or security questions, configured under Advanced > System Tools > Administration. Email recovery is disabled when you log in with a TP-Link ID.

    Try a Previously Linked TP-Link ID or Contact Your ISP

    If you ever bound the router to a TP-Link ID, the login screen offers a toggle. Your cloud account credentials let you in, and you can reset the TP-Link ID password through TP-Link’s account site. Open the Tether app as well, since a linked account often lists the router there.

    For ISP-supplied hardware, call the provider before you reset. ISPs can often push credentials remotely, and a reset can erase the PPPoE username, VLAN tags, or VoIP settings your service depends on.

    Prepare for Lost Settings and Follow the Model’s Reset Instructions

    A factory reset erases the internet connection type, Wi-Fi name and key, port forwards, DHCP reservations, and the admin password. Before you start, write down the details you will need:

    1. ISP login details (PPPoE username and password, or static IP data).
    2. SSIDs and keys, so you can reuse them and avoid reconnecting every device.
    3. Port forwarding and reservation rules.

    With the router powered on, press and hold the Reset button for about 10 seconds until the LEDs flash, then wait for a full reboot. Some models use a pinhole button, and mesh units may need a different hold time, so check the model’s manual. Clearing settings on your computer side can also help when old profiles linger, and our guide on how to reset network settings covers Windows, macOS, and mobile devices. Router setup afterward takes approximately 5 to 10 minutes.

    Set Distinct Passwords and Reconnect Devices Securely

    When the setup wizard asks, give each credential its own value. The admin password, Wi-Fi key, and TP-Link ID password should never match, because anyone who joins your Wi-Fi would otherwise have router control too.

    Store all three in a password manager right away. Enable Password Recovery while you are logged in, and update the firmware. If you keep the old SSID and key, most devices reconnect on their own. Smart home gear stuck on 2.4 GHz sometimes needs to be re-paired.

    Restore Access Without Unnecessary Resets

    Most TP-Link lockouts come down to the wrong credential. Older units accept admin/admin, newer ones expect the password you created, and the label covers only the factory Wi-Fi key.

    Work through the problem in order. Confirm you are on the main network with no VPN running, and find your real gateway. Ping it locally, then try saved passwords, Forgot Password?, or your TP-Link ID. Reset only when all of those fail, and record your ISP details first. After that, the PacketTools diagnostics confirm that your public connection, DNS, and routing came back cleanly.

  • DNS Benchmark: Find Faster, More Reliable DNS Servers

    DNS Benchmark: Find Faster, More Reliable DNS Servers

    PacketTools exists for engineers who want DNS answers they can trust, and picking a resolver is one of the fastest wins you can get on a sluggish network. Every page load starts with name resolution. When your resolver is slow, overloaded, or dropping queries, everything after that first lookup waits, no matter how much bandwidth you pay for.

    A laptop and server rack connected by a network of glowing nodes.

    For Windows users who want the most thorough answer, GRC’s DNS Benchmark v2 is the strongest local option: it measures cached and uncached lookups across IPv4, IPv6, DoH, and DoT resolvers from your own location, and it costs $9.95 one time. If you need something quicker, a browser-based dns speed test gives you a rough ranking in seconds. A command-line tool fits macOS and Linux workflows where you want scripted, repeatable runs.

    Whatever tool you choose, the result only holds for your network, your location, and the time you ran it. With the right metrics and a careful verification step, you can switch resolvers on evidence and confirm the change helped.

    What Should You Measure Before Switching DNS Servers?

    A network engineer reviews abstract performance charts beside server racks.

    You should measure DNS response time for both cached and uncached names, plus how often each resolver times out or returns the wrong answer. Raw ping to a resolver and download speed tell you very little about lookup performance on their own.

    DNS Response Time vs. Ping and Download Speed

    DNS response time is the interval between your query leaving the machine and the answer arriving. Ping measures ICMP round trip to an IP address, which shows network distance but skips the resolver’s own work: cache lookups, recursion to authoritative servers, and validation.

    A resolver can answer ICMP in 8 ms and still take 120 ms to resolve a name it has never seen. Download speed is even further removed, since a fast pipe does nothing for a slow lookup that happens before the first byte moves.

    Treat a ping test as a sanity check for reachability and path length. Use a dedicated DNS tool to measure lookup timing. The impact is large: a slow resolver can add 300 ms or more to every request.

    Cached and Uncached Lookups: Why Both Matter

    A cached lookup returns a name the resolver already holds in memory, so you are measuring network distance plus a hash lookup. An uncached lookup forces full recursion through root, TLD, and authoritative servers.

    Modern pages pull assets from dozens of third-party domains, so cold lookups happen constantly. GRC rebuilt its ranking logic in v2 because v1 exclusively prioritized cached performance, and the newer version weighs uncached lookups at least equally.

    In practice, a large anycast resolver often wins on cached names, while your ISP’s resolver can be competitive on uncached ones because it sits close to you. Look at both columns before you decide.

    Reliability, Timeouts, and Correct Answers

    Speed means nothing if one query in fifty disappears. A lost DNS packet usually costs you a full client retry timeout, often a second or more, which you feel far more than a 10 ms difference in median latency.

    Check three things for each candidate:

    • Lost or timed-out queries during the run
    • NXDOMAIN handling, meaning whether a nonexistent name returns an error or redirects you to an ad page
    • Answer correctness for names you know, including internal names if you rely on split DNS

    GRC’s tool flags resolvers that intercept and redirect bad domain names, which breaks scripts and monitoring that expect a clean failure.

    How Do You Run a Repeatable Test on Your Network?

    A network engineer monitors a repeated test using a laptop, server, and network switch.

    A repeatable test uses the same tool, the same domain list, and the same resolver set, run several times on an otherwise quiet network. You start by recording your current resolver, add a few public alternatives, and compare across different times of day and connection types.

    Choose a Browser-Based or Local Testing Method

    Browser-based tests are fast and need no install, but most of them can only send DNS over HTTPS from the browser. That means you are measuring encrypted performance, which differs from the plain UDP port 53 lookups your OS performs by default.

    Local tools send real resolver queries. Your main options:

    Method Platforms Protocols Best for
    Browser test Any Usually DoH only Quick first look
    GRC DNS Benchmark v2 Windows (Linux via WINE) IPv4, IPv6, DoH, DoT Deep comparison
    net-benchmark CLI Cross-platform UDP, DoH, DoT, DNSSEC checks Scripted, repeated runs
    dig / Resolve-DnsName loop Linux, macOS / Windows Plain DNS Custom domain lists

    GRC v2 tests every resolver with 250 query-sets instead of 50 by default to offset modern internet jitter. Its classic benchmark runs over UDP to port 53, so your firewall must allow that outbound traffic or results will look like total failure.

    Identify Your Current Resolver on Windows, macOS, and Linux

    You cannot judge an alternative until you know your baseline. Check which resolver each OS is using:

    • Windows: run ipconfig /all and read the DNS Servers line, or Get-DnsClientServerAddress in PowerShell.
    • macOS: run scutil --dns and look at resolver #1, or check System Settings > Network > Details > DNS.
    • Linux: run resolvectl status on systemd-resolved systems. If /etc/resolv.conf shows 127.0.0.53, that is the local stub, and the real upstream appears in resolvectl output.

    If the only address listed is your router, such as 192.168.1.1, the router is forwarding to the ISP. Log into it to see the true upstream, and include both the router and the upstream in your test.

    Compare Your Existing DNS Servers With Public Alternatives

    Keep the field small and relevant. Your ISP resolver, your router, and three or four large public resolvers (Cloudflare 1.1.1.1, Google 8.8.8.8, Quad9 9.9.9.9) cover most decisions.

    Add secondary addresses too. Your OS fails over to the secondary when the primary is slow, and a weak secondary drags down real-world experience. GRC notes that your ISP’s servers might be in the wrong order, with the second faster than the first.

    Repeat the Same Workload Across Different Times and Network Conditions

    Run the test at least three times: a quiet morning, an evening peak, and once over Wi-Fi if you normally test on Ethernet. Stop large downloads, backups, and video calls first, since a saturated link drops packets and makes the remote resolver look unreliable.

    Save each run’s export with a timestamp. When evening numbers balloon across every resolver at once, the bottleneck is your link or ISP, and a quick network jitter test during that window helps confirm it.

    How Do You Interpret Results Without Chasing the Lowest Number?

    Pick the resolver with a low median, a tight p95, and near-zero failures across all your runs, even if another one posted a faster single average. A 4 ms win in one test is noise; consistent tail latency is what you feel while browsing.

    Compare Median, p95, and Failure Rates

    The median tells you what a normal lookup costs. The p95 shows the slow tail, the lookups that stall a page. Failure rate tells you how often you hit a retry timeout.

    A resolver with a 15 ms median and a 300 ms p95 will feel worse than one at 22 ms median and 40 ms p95. GRC applies a 95% confidence threshold before recommending a change, which is why its conclusions sometimes list fewer faster resolvers than the bar chart suggests. Apply the same skepticism to your own numbers.

    Account for Resolver Caching and Encrypted Connection Setup

    Your first query to a resolver warms its cache for that domain, so the second run of the same list looks faster. Either clear and randomize names for cold tests or deliberately warm up and discard the first pass. Tools such as net-benchmark offer a warmup option whose results are tagged so you can filter them out.

    Encrypted DNS adds a one-time TLS handshake. DoH and DoT reuse that connection, so steady-state latency approaches plain DNS, but a short test with few queries overweights the handshake. Flush your local resolver cache between runs as well; the steps to flush DNS cache differ per OS.

    Understand Why Location, VPNs, and Test Origin Change the Ranking

    Public resolvers use anycast, so “1.1.1.1” points to whichever site your ISP routes you toward. A colleague in another state, or on another carrier, can get the opposite ranking from yours.

    A VPN moves your test origin to the VPN exit. Results measured over the tunnel describe the VPN path, and the VPN may override your resolver entirely. Test with the VPN off for your home resolver choice, then separately with it on, and run a DNS leak test to see which resolver answers when the tunnel is up.

    Separate Faster Lookups From Better Gaming Ping

    DNS resolves a game server’s name once, at connect time. After that, every packet goes straight to the server’s IP, and your resolver plays no part in in-match latency.

    What a resolver can change is which CDN or matchmaking region you get, since some services hand out addresses based on resolver location. If gameplay lag is the complaint, look at internet latency and path quality to the game server instead of shaving milliseconds off lookups.

    What Security and Privacy Checks Should Accompany Speed Tests?

    Alongside speed, confirm whether each resolver performs DNSSEC validation, whether it supports encrypted transport, and what it logs or filters. A fast resolver that rewrites answers or sells query history is a poor trade.

    DNSSEC Validation Checks Authenticity, Not Confidentiality

    DNSSEC validation lets the resolver verify that signed records came from the zone owner and were not altered in transit. It protects against spoofing and cache poisoning.

    It does nothing to hide your queries. Anyone on the path can still see every name you look up. Test validation by querying a deliberately broken signed domain: a validating resolver returns SERVFAIL, while a non-validating one hands back an address. With dig, the ad flag in a response to a signed domain also indicates validation.

    Compare Plain DNS, DoH, and DoT Under Equivalent Conditions

    Encryption hides your lookups from the local network and ISP. Plain IPv4 and IPv6 DNS offer no security and no privacy, which is why GRC added DoH and DoT benchmarking side by side in v2.

    Compare protocols fairly: same resolver operator, same domain list, same number of queries, and connections allowed to stay open. Comparing Cloudflare over DoH against your ISP over UDP mixes two variables and tells you little about either.

    Review Logging Policies, Filtering, and NXDOMAIN Behavior

    Read each provider’s published privacy policy for how long query logs and source IPs are retained. Filtering resolvers block malware or adult domains, which is useful on purpose and confusing by accident when a legitimate SaaS domain disappears.

    NXDOMAIN rewriting is the quiet one. Query a random nonexistent name like qz7x-test-nonexist.com; anything other than an NXDOMAIN response means the resolver redirects typos to its own page. That behavior breaks software that depends on clean failures and should rule a resolver out for admin work.

    How Do You Apply and Verify a DNS Change Safely?

    Change one device first, confirm it resolves both public and internal names, and only then roll the setting to the router. After the change, verify the active resolver and clear caches so you are testing the new path.

    Update Device or Router Settings Without Breaking Internal DNS

    On a corporate or homelab network, internal names like fileserver.corp.local live on your internal DNS server. Pointing a domain-joined Windows machine at 1.1.1.1 breaks Active Directory logon, group policy, and internal app access immediately.

    For mixed environments, keep clients on internal DNS and change the forwarders on that server to the public resolver you chose. For home networks, set the resolver on one laptop first, then copy it to the router so every device inherits it. The menus differ per OS, and the steps to change DNS settings on Windows, macOS, and Linux cover each. Always set a secondary from a different operator or a second address from the same one.

    Confirm the Active Resolver and Account for Local Caches

    Settings screens show what you configured, which is not always what is in use. Verify the live path:

    • Windows: Resolve-DnsName example-domain -Type A and check ipconfig /all; clear with ipconfig /flushdns.
    • macOS: scutil --dns, then sudo dscacheutil -flushcache; sudo killall -HUP mDNSResponder.
    • Linux: resolvectl status and resolvectl flush-caches.

    Browsers keep their own cache and may use built-in DoH that bypasses the OS entirely. Check Chrome, Edge, or Firefox secure DNS settings before concluding the OS change failed.

    Use PacketTools DNS Lookup and Propagation Checks to Investigate Unexpected Answers

    When a site resolves to a different IP after the switch, compare answers instead of guessing. PacketTools DNS Lookup shows the records a name returns, and the DNS propagation checker shows what resolvers in other regions see.

    If your new resolver returns an address nobody else does, you are looking at filtering, a stale cache, or geo-based CDN steering. If every region agrees and only your machine differs, the problem is local cache or a hosts file entry. For persistent failures, the broader steps to troubleshoot DNS issues narrow it down. PacketTools logs none of these queries, which keeps internal hostnames you test out of third-party records.

    Check Routing and Latency When DNS Is Not the Bottleneck

    If lookups are fast and pages still crawl, DNS is done and the path is the problem. Run a traceroute to the slow site and look for the hop where latency jumps and stays high, or where packet loss persists to the destination.

    Loss that shows at one middle hop but clears afterward is usually ICMP rate limiting, not a fault. Steady loss from a hop onward points to congestion or a bad link, and knowing how to trace a route properly helps you hand your ISP evidence instead of complaints.

    Choose Consistent DNS Performance Over a One-Time Win

    The resolver worth keeping is the one with steady DNS response time across quiet hours, peak hours, and both wired and wireless connections. A single dns benchmark run captures one moment on one path; three or four saved runs show you the pattern.

    Weigh results in this order:

    1. Failure rate near zero
    2. p95 latency low and stable
    3. Median latency for cached and uncached names
    4. Security behavior: DNSSEC validation, encrypted transport, clean NXDOMAIN responses

    Apply the winner on one device, verify the active resolver, then move it to the router or your internal forwarders. Re-run the same test a week later with the same domain list; if the numbers hold, the change is settled, and if they drift, your saved exports show exactly when.

  • Internet Latency: What It Means, How to Test and Fix It

    Internet Latency: What It Means, How to Test and Fix It

    You notice internet latency long before you can name it: the voice that talks over you on a call, the game shot that lands a beat late, the web page that pauses before anything happens. Your speed test can show hundreds of megabits per second while the connection still feels sluggish, because speed and delay are separate measurements.

    A person waits at a desk as a video call freezes on a computer screen.

    Internet latency is the time, in milliseconds, that data takes to reach a destination and return. To fix it, you measure round-trip time with a ping test against your router and an internet host, compare the results, and treat the segment where the delay appears. Under about 50 ms feels responsive for nearly everything; spikes and jitter are what usually ruin calls and games.

    PacketTools builds its diagnostics from nearly three decades of production network work, and its tools run in real time with no sign-in and no logging of your IP addresses, queries, or test data. Once you know how to read a latency result, you can tell whether the lag lives on your Wi-Fi, inside your router’s queues, or out on your ISP’s path, and you can bring evidence to whoever owns that segment.

    What Does Latency Measure, and How Is It Different From Speed?

    A person uses a laptop for a video call beside a Wi-Fi router.

    Latency measures delay: how long a packet takes to travel between two points. Speed, in the way ISPs advertise it, measures capacity. A complete picture needs both, plus two stability metrics that ping tools report alongside the delay itself.

    One-Way Delay vs. Round-Trip Time

    One-way delay is the time a packet takes to go from your device to a destination. Round-trip time (RTT) adds the return trip. Almost every consumer tool, including ping, reports RTT, because measuring one-way delay accurately requires tightly synchronized clocks on both ends.

    RTT is roughly double the one-way delay, though the two directions can differ. Your upload path and the return path may cross different routers and sit in different queues. A ping is not an exact measure of directional latency for exactly this reason.

    In practice, RTT is the number you want. Every interactive action you take (a keystroke in a remote session, a click in a game) needs a request and a response, so RTT reflects what you feel.

    Latency vs. Bandwidth: Why Fast Downloads Can Still Feel Slow

    Bandwidth is the size of the pipe, measured as download speed and upload speed in Mbps or Gbps. Latency is how long each trip through the pipe takes. A 1 Gbps plan with 150 ms of RTT downloads large files quickly, yet a video call on it still stutters.

    Web browsing exposes the gap clearly. A single page triggers a DNS lookup, a TCP handshake, and a TLS negotiation before content arrives, and subsequent requests have less latency once the connection is set up. Each of those steps costs one or more round trips, so a page with dozens of assets multiplies your RTT many times over. Doubling bandwidth barely changes that load time; halving RTT changes it a lot.

    Ping, Jitter, and Packet Loss: What Each Metric Reveals

    Each metric points at a different kind of problem:

    Metric What it measures What a bad value feels like
    Ping (RTT) Average delay to a host and back Sluggish response, input lag
    Jitter Variation between consecutive delays Choppy audio, robotic voices, rubber-banding
    Packet loss Percentage of packets that never return Freezes, dropped calls, retransmission stalls

    Jitter often hurts more than a steady high ping, because real-time apps size their buffers around predictable delay. You can check variability directly with a network jitter test. Packet loss compounds both: TCP retransmits lost data, which adds delay, while voice and video apps drop it and fill the gap with glitches.

    What Is a Good Latency for Your Applications?

    A software professional works at a laptop beside a wireless router.

    For most home and office use, an RTT under 50 ms to nearby servers with jitter under about 10 ms is good latency. Real-time apps care most about consistency, while streaming cares mostly about sustained throughput.

    How to Interpret Common Ping Ranges

    Use these ranges for a nearby, same-region destination:

    • Under 20 ms: Excellent. Typical of fiber and wired connections to a local server.
    • 20–50 ms: Good low latency for gaming, calls, and remote desktops.
    • 50–100 ms: Usable, with noticeable lag in competitive games and occasional talk-over on calls.
    • 100–200 ms: High latency. Interactive apps feel delayed.
    • Over 200 ms: Poor for anything real-time; expected only on long intercontinental paths or geostationary satellite.

    Distance sets a floor you cannot tune away. Light in fiber travels at about 200,000 km/s, roughly 5 ms of RTT per 500 km of cable path, so a coast-to-coast US ping in the 60–80 ms range is normal.

    What Online Gaming, Video Calls, and Remote Work Need

    Online gaming is the most sensitive. Competitive shooters feel best under 30 ms, and anything with frequent spikes above 100 ms causes rubber-banding even when the average looks fine.

    Video calls tolerate more. Conversations stay natural up to around 150 ms one way, and the platforms buffer to smooth jitter. Above roughly 300 ms of RTT, people start interrupting each other.

    Remote work tools vary by type. Remote desktop and VDI sessions behave like games, where every keystroke waits for a round trip, so 50 ms or less keeps typing crisp. File sync and email barely care about latency at all.

    Why Average Latency Can Hide Spikes

    A test that reports “average latency: 28 ms” can hide a connection that sits at 15 ms most of the time and jumps to 400 ms every few seconds. The spikes are what freeze your call.

    Always look at the minimum, maximum, and jitter values together. In production troubleshooting, a wide gap between minimum and maximum RTT almost always points to queueing (congestion or bufferbloat) and rarely to distance. Distance raises the minimum; queues stretch the maximum.

    Why 4K Streaming Depends More on Sustained Throughput

    4K streaming needs steady bandwidth, commonly around 25 Mbps per stream, and tolerates high latency well. The player downloads several seconds of video ahead of time, so a 150 ms RTT only affects how fast playback starts.

    If your 4K stream buffers, check throughput and packet loss first. Latency becomes relevant for streaming only during live, interactive formats such as watch parties or live sports with chat.

    How Do You Test Latency and Locate the Delay?

    You locate the delay by testing more than one hop: your router, then an internet host, under different conditions, over time. A single number from one test tells you that latency exists; a set of comparisons tells you where it lives.

    Start With PacketTools Ping Test and Confirm the Test Origin

    Run the PacketTools ping test against a well-known host and note the minimum, average, maximum, and loss. It uses ICMP echo requests, the same mechanism as the command-line ping, and nothing about your query is logged or stored.

    Check where the test originates. A browser-based tool may send probes from a server, which measures that server’s path to the target, while a ping from your own terminal measures your path. Confirm your public IP address too, so you know whether a VPN or proxy is in the path. A VPN exit in another region can add 30–100 ms on its own, and it is the first thing to rule out.

    Compare Local Gateway and Internet Destination Measurements

    Ping your own router next. Find your router IP address (often 192.168.1.1 or 192.168.0.1) and run a continuous ping:

    • Windows: ping -t 192.168.1.1
    • macOS/Linux: ping 192.168.1.1

    Leave it running beside a ping to an internet host such as 1.1.1.1. Then read the pair:

    Router RTT Internet RTT Likely location of the problem
    Under 5 ms, stable High or spiky ISP, modem, or upstream path
    Spiky or lossy Spiky or lossy Your Wi-Fi, cabling, or device
    Under 5 ms, stable Fine at idle, spikes under load Bufferbloat in your router or modem

    A wired router ping should sit at 1 ms or below. On Wi-Fi, 2–10 ms is normal, but jumps to 50 ms or more point straight at the wireless link.

    Repeat Tests Over Ethernet and Wi-Fi, Idle and Under Load

    Run the same pair of pings four ways: Ethernet idle, Ethernet under load, Wi-Fi idle, Wi-Fi under load. To create load, start an internet speed test or a large download while the pings run.

    Loaded latency is the result most people never measure. If idle RTT is 15 ms and it climbs past 200 ms during a speed test, your connection suffers from bufferbloat, and that explains why calls fall apart when someone in the house starts a backup or game download. Cloudflare’s speed test reports loaded latency during downloads and uploads, though it receives your IP address and an estimated location as part of the test.

    Track Results Over Time and Use Traceroute for Context

    Connection latency changes by hour. Repeat your tests in the morning, mid-afternoon, and during the 7–11 p.m. peak, and record min/avg/max and loss each time. Latency over time that rises only in the evening points to congestion at your ISP’s node or peering links.

    When the internet leg is the problem, a traceroute shows the hops your packets cross and the delay at each. Learning how to trace a route helps you avoid a common misread: a single hop with high RTT that does not carry forward to later hops is a router deprioritizing ICMP replies. Delay that appears at one hop and persists to the destination marks the real problem segment.

    What Causes High or Unstable Latency?

    Unstable latency comes mostly from queues and radio contention close to you, while high but stable latency comes from distance, routing, and your access technology. Your test pairs from the previous section tell you which group you are dealing with.

    Wi-Fi Interference, Device Load, and Local Network Faults

    Wi-Fi is a shared, half-duplex medium: only one device transmits on a channel at a time, and every neighbor’s network on the same channel competes for airtime. Retransmissions after interference show up as jitter. The 2.4 GHz band suffers most, since microwaves, Bluetooth, and dozens of overlapping networks crowd its three non-overlapping channels.

    Weak signal makes it worse. A device at the edge of coverage drops to slow modulation rates and occupies the air longer for every frame. If you check Wi-Fi speed in different rooms, the rooms with low throughput are usually the ones with spiky ping too.

    Device-side problems also appear as latency. A laptop running a cloud backup, an outdated wireless driver, or aggressive power-saving on the network adapter adds delay before packets leave the machine. Keeping current with network driver updates removes a surprising number of “Wi-Fi” complaints. Damaged Ethernet cables and failing switch ports cause loss and retransmits that mimic ISP trouble.

    Network Congestion and Bufferbloat

    Network congestion happens when traffic exceeds a link’s capacity and packets wait in queues. Bufferbloat is the specific case where a router or modem holds oversized buffers, so packets wait hundreds of milliseconds instead of being dropped or paced.

    The signature is unmistakable in your tests: idle ping looks healthy, and loaded ping explodes. Upload congestion is the usual culprit on cable and DSL, because upstream capacity is small. A single video upload or cloud sync can saturate it, and every packet you send, including the TCP acknowledgments your downloads depend on, waits behind that traffic.

    Distance, Routing, and ISP Peering

    Physics sets a minimum delay. US traffic to a server in Europe crosses roughly 6,000 km or more of fiber each way, so RTT in the 70–100 ms range is expected before any congestion exists.

    Routing adds to that floor. BGP selects paths by policy and business agreements, so traffic between two nearby cities sometimes travels through a distant exchange point. When your ISP’s peering with a content network is congested, latency to that one service rises at peak hours while everything else looks normal. Traceroute exposes this as delay starting at a hop between two networks.

    How Fiber, Cable, DSL, Cellular, and Satellite Access Differ

    Your access technology sets the baseline:

    Access type Typical added latency Notes
    Fiber internet Lowest, often under 10 ms to first hop Symmetric upload reduces bufferbloat
    Cable internet Low to moderate Shared node; evening congestion and upload bufferbloat are common
    DSL Moderate Interleaving for error correction adds delay
    5G home internet Moderate, variable Signal quality and tower load drive jitter
    Satellite (geostationary) Very high, 600 ms+ RTT Distance to orbit makes real-time use difficult
    Satellite (Starlink, LEO) Roughly 20–40 ms on short routes Brief spikes during satellite handoffs

    If your access type carries a high baseline, no home network tuning will drop RTT below it. Focus instead on the jitter and loaded latency you can control.

    How Can You Reduce Latency Without Guesswork?

    You reduce latency by fixing the segment your tests identified, starting with the cheapest local changes and moving outward. Wired connections and queue management solve most home cases; the remainder needs server choice or ISP action.

    Fix Local Issues With Ethernet, Better Wi-Fi, and Healthy Hardware

    An Ethernet cable is the single most effective latency fix for a desk-bound gaming PC, work laptop, or console. It removes airtime contention entirely, and router RTT drops to around 1 ms with near-zero jitter.

    Where you must use Wi-Fi:

    1. Move latency-sensitive devices to 5 GHz or 6 GHz and away from crowded 2.4 GHz.
    2. Place the router centrally and in the open, out of cabinets and away from metal.
    3. Replace range extenders with a wired-backhaul mesh, since wireless repeaters halve airtime and add a hop.
    4. Pick a less congested channel manually if auto-selection keeps landing on a busy one.

    Reboot the modem and router to clear a stuck state, then retest. If a single device lags while others are fine, resetting network settings on that device often clears corrupted adapter configurations. Routers older than about five years frequently lack the CPU to shape traffic at modern speeds and are worth replacing.

    Manage Loaded Latency With QoS and Smart Queue Management

    Quality of service (QoS) prioritizes some traffic over other traffic, but classic priority rules do little against bufferbloat, because the bloated buffer usually sits in the modem, beyond the router’s control.

    Smart queue management (SQM) fixes that. Algorithms such as fq_codel and CAKE keep queues short and give each flow a fair turn. To make them work, set the shaper slightly below your measured line rate, around 90–95% of download and upload, so the queue forms in your router where SQM manages it. Many current routers expose this as “SQM,” “Smart Queue,” or an anti-bufferbloat toggle. After enabling it, rerun your loaded test: a jump from 15 ms to 300 ms under load should shrink to a rise of only a few milliseconds.

    Choose Closer Servers and Give Your ISP Actionable Evidence

    Server choice is free latency. Select the nearest game region, the closest VPN exit, and the nearest data center for cloud desktops. A server in your region versus one across the country can mean a difference of 50 ms or more.

    When tests point past your router, your ISP owns the problem, and evidence speeds up the fix. Bring:

    • Timestamped ping results to your gateway and to an internet host, wired
    • Peak versus off-peak comparisons over several days
    • A traceroute showing the hop where delay begins and persists
    • Packet loss percentages from the first ISP hop onward

    Support teams act faster on “18 ms at 10 a.m., 140 ms at 9 p.m., starting at your hop 3” than on “my internet is laggy.” A structured network troubleshooting record also keeps you from repeating the same tests on every call.

    When Can Wi-Fi 7, MLO, and L4S Help?

    Wi-Fi 7 brings Multi-Link Operation (MLO), which lets a device send across multiple bands at once and switch to whichever is clear. That cuts jitter in congested environments, but only when both the router and your device support Wi-Fi 7.

    L4S (Low Latency, Low Loss, Scalable Throughput) is an IETF standard that marks traffic so network queues signal congestion early, keeping delay low even under heavy load. It needs support from the application, your operating system, and your ISP’s network. Some US cable providers have begun deploying it. Neither technology removes distance or fixes a bad cable, so test first and treat upgrades as targeted fixes for a measured problem.

    Measure the Delay, Fix the Cause, and Retest

    A latency test is useful only when you can compare it against something: your router versus the internet, Ethernet versus Wi-Fi, idle versus loaded, morning versus evening. Those comparisons point to one segment, and each segment has its own fix: cabling or Wi-Fi placement locally, smart queue management for bufferbloat, a closer server for distance, and documented evidence for your ISP.

    Keep your baseline numbers. A wired ping to your router should sit at about 1 ms, and loaded latency should rise only a few milliseconds over idle. After every change, rerun the same ping test under the same conditions and compare min, average, max, and loss against those baselines. PacketTools’ network tools cover each of those comparisons, so your before-and-after numbers come from the same measurement each time and show whether you reached low latency or only moved the problem.

  • Reset Network Settings in Windows 11 and Windows 10

    Reset Network Settings in Windows 11 and Windows 10

    The fastest way to fix a Windows PC that won’t stay online is to work from the smallest repair to the largest, and Windows’ built-in Network reset sits at the far end of that ladder. It removes every installed network adapter, reinstalls each one with default settings, and returns Winsock and TCP/IP to their original state after a restart.

    A hand uses a smartphone beside a wireless router.

    To reset network settings in Windows 11, open Settings > Network & internet > Advanced network settings > Network reset > Reset now; in Windows 10, the same button lives under Settings > Network & Internet > Status. Both paths restart your PC and clear custom configuration, so VPN clients, proxy entries, static IPs, and saved Wi-Fi passwords need attention afterward.

    That trade-off is why the order of operations counts. Many network connectivity issues come from a stale DNS cache, an expired DHCP lease, or one misbehaving driver, and each of those has a narrower fix that leaves the rest of your configuration alone. PacketTools builds its free diagnostics and network troubleshooting guidance around that same habit from production networks: confirm the fault, apply the smallest repair, then verify the result from outside the machine.

    Use Windows Settings for a Full Reset

    A full reset through Windows Settings takes about two minutes of clicking plus one restart, and it wipes adapter-level configuration on every interface at once. Record your custom settings first, then follow the path for your Windows version and plan for reconnection work after the reboot.

    What Should You Save Before Proceeding?

    Anything you configured by hand disappears, so capture it before you click Reset now. Open an elevated Command Prompt and run ipconfig /all > %USERPROFILE%Desktopnetconfig.txt to save a text snapshot of every adapter.

    Check this list against your machine:

    • Static IP details: address, subnet mask, default gateway, and custom DNS servers for each adapter.
    • Saved Wi-Fi passwords: run netsh wlan show profiles to list networks, and confirm you know the password for any you depend on.
    • VPN connections: server addresses, authentication method, and any installer or configuration file your VPN client needs.
    • Proxy settings: proxy address, port, and any setup script URL from Settings > Network & internet > Proxy.
    • Virtual switches: Hyper-V, WSL, or lab adapters you created yourself.
    • Driver installer: a copy of your Wi-Fi and Ethernet driver from the PC maker’s site, saved locally.

    If you troubleshoot on a corporate laptop, check with your IT team before resetting. A remote machine that loses its VPN loses its path back to management tools.

    Windows 11: Find Network Reset Under Advanced Network Settings

    To reset network settings in Windows 11, follow these steps:

    1. Press Windows + I to open Settings.
    2. Select Network & internet in the left pane.
    3. Scroll down and choose Advanced network settings.
    4. Under More settings, select Network reset.
    5. Read the description, then select Reset now.
    6. Confirm with Yes.

    You can jump straight to step 4 by running start ms-settings:network-advancedsettings from Command Prompt or the Run dialog. Save open work before confirming, because Windows signs you out and restarts on its own after a short warning.

    Windows 10: Find Network Reset Under Status

    To reset network settings in Windows 10, the option sits on the Status page:

    1. Open Start > Settings.
    2. Select Network & Internet.
    3. Choose Status in the left pane.
    4. Scroll to the bottom and select Network reset.
    5. Select Reset now, then Yes.

    Network reset arrived with the Windows 10 Anniversary Update (version 1607), so any supported Windows 10 build has it. If you can’t find the link, confirm you’re on the Status page; on smaller screens it sits below the Advanced network settings group.

    What Changes After Windows Restarts?

    Expect to come back to a PC with no active connection. Your network adapters have been removed and reinstalled, so Wi-Fi shows nearby networks and waits for you to pick one and enter its password again.

    Here’s what to check in the first few minutes:

    Item Status after reset What you do
    Wired Ethernet with DHCP Reconnects on its own Confirm you have an IP address
    Saved Wi-Fi networks Need reconnecting Select the network, enter the password
    Static IP or custom DNS Reverted to automatic Re-enter from your saved notes
    VPN clients and virtual switches Need reinstalling or reconfiguring Run the installer or import the profile
    Proxy settings Cleared Re-enter address and port
    Network profile May switch to Public Set it back to Private on trusted networks

    Test plain connectivity before you reinstall VPN software. That way you know whether the reset itself fixed the fault or whether the VPN layer was the trigger.

    Could a Less Disruptive Fix Restore Your Connection?

    A person checks a smartphone beside a laptop at a home-office desk.

    Yes, in most cases a targeted fix brings you back online without touching the rest of your configuration. Start by deciding whether the fault belongs to your PC at all, then let Windows diagnose itself, then restart just the adapter that’s failing.

    Check Whether the Fault Affects One PC or Every Device

    Grab your phone or a second laptop and connect it to the same network. If every device struggles, the problem sits upstream at the router, modem, or ISP, and resetting Windows changes nothing.

    For an upstream fault, power-cycle the modem and router: unplug both, wait at least 30 seconds, plug the modem in first, and wait for its lights to settle before powering the router. You can also log in to your router’s IP address and check the WAN status page for an ISP connection.

    If only your PC fails, narrow it further:

    • One network only: forget it under Settings > Network & internet > Wi-Fi > Manage known networks, then reconnect.
    • Every network fails: the problem lives in this Windows installation, so keep going down this guide.
    • Connected icon, nothing loads: that pattern points at DNS or routing, covered in the guide to Wi-Fi connected but no internet.
    • Wi-Fi keeps disconnecting: try the other band (2.4 GHz or 5 GHz) to rule out interference before blaming Windows.

    Run the Windows Network Troubleshooter

    The built-in troubleshooter catches ordinary misconfigurations, such as a disabled adapter or Airplane mode left on, in under a minute. On Windows 11, Microsoft puts it first: open the Get Help app, search for connect to network and internet, and run the Network and Internet diagnostics.

    On Windows 10, right-click the network icon in the taskbar and choose Troubleshoot problems. Note anything the troubleshooter reports even if it says it couldn’t fix the issue; messages like “DNS server isn’t responding” tell you exactly which component to target next.

    Restart One Wi-Fi or Ethernet Adapter Without Resetting Everything

    Disabling and re-enabling a single adapter clears a stuck interface while leaving its configuration intact. In administrator PowerShell, run:

    Get-NetAdapter
    Restart-NetAdapter -Name "Wi-Fi"

    Replace Wi-Fi with the name shown in the first command. Prefer the GUI? Press Windows + R, type ncpa.cpl, right-click the adapter in Network Connections, choose Disable, wait ten seconds, then choose Enable.

    This step resets the network adapter’s link state only. Your static IP, DNS servers, and saved profiles all survive, which makes it the right move when connectivity drops after sleep or a dock change.

    Repair Specific Network Components With Commands

    A technician works on a laptop connected to a network router and switch.

    Command-line repairs let you fix the exact layer that’s broken, whether that’s name resolution, the socket catalog, the IP stack, or address assignment. Microsoft’s own Wi-Fi guidance runs netsh winsock reset, netsh int ip reset, ipconfig /release, ipconfig /renew, and ipconfig /flushdns in that order, but you can also run each one alone when you know the symptom.

    Open Search, type Command Prompt, choose Run as administrator, and approve the prompt before running any of the commands below.

    Clear the Local DNS Cache With ipconfig /flushdns

    Run ipconfig /flushdns when some sites load and others fail, or when a site moved servers and your PC still points at the old address. The command empties cached lookups, including cached failures, and leaves your configured DNS server addresses untouched.

    PowerShell users can run Clear-DnsClientCache, which does the same job, so there’s no need to run both. A full walkthrough for every platform sits in the guide on how to flush your DNS cache.

    Flushing takes effect instantly with no restart. If the same site fails right after a flush, the bad answer is coming from your DNS server itself.

    Reset Winsock With netsh winsock reset

    Run netsh winsock reset when apps report socket errors, or when connectivity broke after you uninstalled a VPN, firewall, or security suite. Those products install Layered Service Providers into the Winsock catalog, and a leftover entry can block every app from opening a connection.

    The reset rebuilds the catalog to defaults. Restart Windows afterward; the change doesn’t apply until you do. Any security product that depended on its own LSP needs a reinstall or repair once you’re back online.

    Restore TCP/IP Defaults With netsh int ip reset

    Run netsh int ip reset when the IP stack itself looks damaged: adapters show odd addresses, routes go missing, or ipconfig reports settings you never configured. The command rewrites TCP/IP registry values to their defaults.

    Two cautions from experience:

    • It clears static IP assignments on affected interfaces, so have your saved ipconfig /all output ready.
    • An “Access is denied” line for one registry key is common and harmless; check whether the rest of the output reports success.

    Restart after this command too. If you plan to run both netsh resets, run them back to back and restart once.

    Renew a DHCP Lease Only When Automatic Addressing Is Enabled

    ipconfig /release followed by ipconfig /renew asks your router for a fresh address. It helps when your PC shows a 169.254.x.x address or holds a lease from a network you’ve left. If DHCP is new territory, the short version is that your router hands out addresses automatically, and these commands restart that exchange.

    Skip these commands on an adapter with a static IP; they won’t help and can leave the interface without an address. To target one adapter, add its name: ipconfig /renew "Wi-Fi". For DHCPv6, use ipconfig /release6 and ipconfig /renew6.

    Run release and renew from a local session. Releasing the address on a remote machine cuts off your own connection.

    When Should You Repair the Network Adapter Driver?

    Repair the driver when the adapter itself misbehaves: it disappears, shows an error, or failed right after a Windows or driver update. Device Manager tells you which case you’re in, and a saved offline installer keeps the repair from stranding you.

    Check Device Manager for Adapter Errors

    Press Windows + X and choose Device Manager, then expand Network adapters. Look for these signs:

    • Yellow triangle: the driver loaded with an error. Double-click the adapter and read the Device status box for a code such as Code 10 or Code 43.
    • Down arrow: the device is disabled. Right-click and choose Enable device.
    • Adapter missing: select View > Show hidden devices, then Action > Scan for hardware changes.
    • Unknown device under Other devices: Windows has no driver at all.

    A clean entry with no warning points you back toward configuration fixes. An error code points at the network adapter driver.

    Choose Between Updating, Rolling Back, and Reinstalling the Driver

    Match the action to how the fault started:

    Situation Action Where
    Fault began after a driver update Roll back Properties > Driver > Roll Back Driver
    Old driver, intermittent drops Update Install the latest from the PC or chipset maker
    Error code, corrupted install Reinstall Uninstall device, then restart

    To reinstall the network driver, right-click the adapter, choose Uninstall device, tick Attempt to remove the driver for this device, and restart. Microsoft notes that Windows automatically installs the driver again after the restart in most cases. For vendor-specific steps, the guide on how to update network drivers covers Intel, Realtek, and Qualcomm adapters.

    Prefer the manufacturer’s driver over the generic Windows Update version for Wi-Fi cards; vendor builds carry roaming and power-management fixes the inbox driver lacks.

    Keep an Offline Driver Installer Before Removing Anything

    Download the correct driver before you uninstall anything, because a PC without a working adapter can’t fetch one. Note your PC maker and model number (run wmic csproduct get name or check the sticker underneath), then grab the Wi-Fi and Ethernet drivers from the maker’s support page.

    Save the installers to the local drive and to a USB stick. If the current machine is already offline, download them on another computer. With that copy in hand, a failed automatic reinstall costs you five minutes instead of an afternoon.

    Verify Recovery and Isolate Any Remaining Fault

    Confirm recovery from the inside out: local addressing first, then the wider internet, then your custom configuration. If something still fails, the checks below give you the evidence to pinpoint where.

    Confirm the Local IP Address, Gateway, and DNS Configuration

    Run ipconfig /all and read the entry for your active adapter. A healthy DHCP client shows:

    • An IPv4 address in your LAN range, such as 192.168.1.x (a 169.254.x.x address means DHCP failed).
    • A default gateway, usually your router.
    • One or more DNS servers.
    • DHCP Enabled: Yes, unless you deliberately run a static IP address.

    Then run ping against the gateway address. Replies with low single-digit millisecond times mean your PC reaches the router. If the gateway answers but websites don’t, test name resolution with nslookup packettools.com.

    Use PacketTools to Check Public IP, DNS, and External Reachability

    Local checks prove your PC reaches the router; browser-based tests prove traffic leaves your network correctly. PacketTools runs these checks in real time with no sign-in, and it doesn’t log or store your IP, queries, or test data.

    Work through them in order:

    1. What Is My IP: confirms your public address and shows whether traffic exits through a VPN or your ISP.
    2. DNS Lookup: confirms domains resolve to the expected addresses. If they don’t, the steps to troubleshoot DNS issues pick up from there.
    3. Ping test: measures reachability and latency to a host.
    4. Traceroute: shows where packets stop. Learning how to trace a route helps you tell an ISP hop failure from a local one.

    Restore Required VPN Settings and Review the Network Profile

    Once basic connectivity tests clean, bring back the custom layers one at a time. Reinstall or reconfigure your VPN client, connect, and repeat the public IP check to confirm traffic routes through the tunnel.

    Re-enter proxy settings under Settings > Network & internet > Proxy if your organization uses one. Then open your Wi-Fi or Ethernet properties and check the network profile: a reset can leave it on Public, which blocks file sharing and network discovery on your home or office LAN. Set trusted networks to Private.

    If connectivity breaks the moment the VPN connects, the VPN layer is your fault source, and resetting Windows again won’t keep it fixed.

    Escalate Persistent Failures With Useful Diagnostic Evidence

    When nothing above holds, hand your ISP or IT team evidence they can act on. For Wi-Fi faults, run netsh wlan show wlanreport from an elevated prompt; it generates an HTML report of recent sessions and disconnect reasons.

    Collect these before you escalate:

    • Exact times of each failure.
    • Adapter model, driver version, and driver date from Device Manager.
    • Windows build and recent update history.
    • ipconfig /all output and traceroute results.
    • What you already tried, in order.

    A reset that you have to repeat every few days points at something reintroducing the bad state, such as a driver, security agent, or policy, and that detail helps the next person most.

    Choose the Smallest Fix That Restores Reliable Connectivity

    Start with the repair that touches the least and move up only when it fails. Check whether other devices share the fault, run the troubleshooter, restart the single adapter, then use the targeted commands for DNS, Winsock, TCP/IP, or DHCP.

    Move to the driver when Device Manager shows errors or the fault followed an update. Save the full option to reset network settings for cases where every adapter-level fix has failed or networking broke across multiple networks, and record your static IPs, VPN details, and driver installer before you press Reset now. After any fix, confirm your gateway, DNS, and public IP before restoring VPN and proxy settings one at a time.

  • Change DNS Settings on Windows, Mac, Mobile, and Routers

    Change DNS Settings on Windows, Mac, Mobile, and Routers

    PacketTools runs browser-based DNS diagnostics without logging a single query, and the same habits that keep those tools honest apply to your own machines: know which resolver answers your lookups, change it on purpose, and confirm the result. To switch, open your device’s network settings, set DNS from automatic to manual, and enter a primary and secondary resolver address.

    A network administrator adjusts a laptop beside a wireless router.

    To change DNS settings, open the network adapter or Wi-Fi properties on your device (or the WAN/Internet page on your router), switch DNS assignment to Manual, and enter a trusted resolver pair such as Cloudflare’s 1.1.1.1 and 1.0.0.1 or Google Public DNS’s 8.8.8.8 and 8.8.4.4. A device-level change affects one machine and is easy to undo. A router change pushes the new resolver to every device that gets its address from the router.

    Every step below includes the path back to your original configuration. A DNS change that breaks name resolution looks exactly like an internet outage, so the rollback is as important as the switch.

    When Does a Different DNS Resolver Help?

    A person reviews network settings on a laptop beside a wireless router.

    A different resolver helps when your current DNS server is slow, unreliable, filtering things you don’t want filtered, or keeping logs you’d prefer it didn’t. The domain name system translates a domain name into an IP address, and by default your device asks whichever DNS server your internet service provider (ISP) hands out through DHCP.

    Swapping that server changes who answers your lookups and what policies they apply. It leaves your connection speed, routing, and public address untouched.

    What Can a DNS Change Fix, and What Can’t It?

    A resolver change fixes problems that live in the lookup step. Good candidates include:

    • ISP resolver outages or timeouts, where pages hang on “Resolving host” while ping to a numeric address works fine
    • Stale or incorrect answers from a poorly maintained ISP cache
    • Unwanted ISP redirection, such as typo domains landing on an ad-filled search page
    • Missing security filtering, when you want a resolver that blocks known malware and phishing domains
    • Privacy preferences, when you’d rather send queries to a provider with a published no-logging policy

    A DNS change does not increase internet bandwidth, encrypt all internet traffic, or change your public IP address. Packet loss, a weak Wi-Fi signal, a saturated uplink, and a down fiber line all stay exactly as they were. If you’re fuzzy on how addressing and name resolution fit together, the basics of IP addresses clear that up quickly.

    A quick test separates the two: if ping 1.1.1.1 succeeds but ping packettools.com fails, you have a DNS problem. If both fail, start broader network troubleshooting before touching resolver settings.

    Which Public DNS Servers Should You Consider?

    Public DNS servers from large providers run anycast networks with redundant nodes, which is why they’re common choices for a switch. These are the published addresses for the most widely used options:

    Provider IPv4 primary IPv4 secondary IPv6 primary Notable for
    Cloudflare 1.1.1.1 1.0.0.1 2606:4700:4700::1111 Speed, privacy policy
    Google Public DNS 8.8.8.8 8.8.4.4 2001:4860:4860::8888 Reliability, global reach
    Quad9 9.9.9.9 149.112.112.112 (provider-published) Malware and phishing blocking
    OpenDNS (Cisco) 208.67.222.222 208.67.220.220 2620:119:35::35 Content filtering
    OpenDNS FamilyShield 208.67.222.123 208.67.220.123 (provider-published) Adult content blocking

    Pick one provider and use its own primary and secondary pair. Mixing a filtering resolver with a non-filtering one produces inconsistent results, because your device may fall back to the secondary and skip the filter entirely.

    Read the provider’s current privacy and logging policy before you commit. Public resolvers differ in what they keep, and speed claims say nothing about data handling.

    How Do You Set DNS on Windows 11 and Windows 10?

    Windows gives you four routes: the Settings app, the classic Control Panel, PowerShell, and netsh in Command Prompt. All of them write the same per-adapter setting, so choose the one that fits whether you’re fixing one laptop or scripting a fleet. Changing DNS requires an administrator account.

    Before you start, run ipconfig /all and note the current DNS Servers line for your active adapter. That’s your rollback record.

    Use the Windows 11 Settings App for Wi-Fi or Ethernet

    To change DNS on Windows 11 through the Settings app:

    1. Right-click Start and choose Settings.
    2. Select Network & internet.
    3. For Wi-Fi, choose Wi-Fi, then Hardware properties (or your network’s properties). For a wired link, choose Ethernet.
    4. Next to DNS server assignment, click Edit.
    5. Change the dropdown from Automatic (DHCP) to Manual.
    6. Turn on IPv4.
    7. Enter the Preferred DNS address (for example, 1.1.1.1) and the Alternate DNS address (1.0.0.1).
    8. Click Save.

    The setting applies per network. If you set it on your home Wi-Fi, a coffee shop network or your Ethernet adapter still uses whatever DHCP hands out. Switching back means returning the dropdown to Automatic (DHCP). If you’ve ever set a static address on that adapter, the difference between DHCP and static IP assignment explains why the DNS fields sometimes stay locked to manual.

    Use Control Panel on Windows 10 or Windows 11

    The Control Panel route works on both versions and exposes the classic TCP/IPv4 dialog many admins prefer:

    1. Open Control Panel and go to Network and Sharing Center.
    2. Click Change adapter settings.
    3. Right-click your active network adapter and choose Properties.
    4. Select Internet Protocol Version 4 (TCP/IPv4) and click Properties.
    5. Choose Use the following DNS server addresses.
    6. Fill in Preferred DNS server and Alternate DNS server.
    7. Click OK, then Close.

    A tip from production work: tick Validate settings upon exit if you see it. It won’t catch a typo in a resolver address, but it flags a broken adapter configuration before you close the window and lose your connection.

    Use PowerShell or Command Prompt for Repeatable Changes

    PowerShell is the fastest way to make the same change across machines. Open Terminal (Admin) and find your interface index:

    Get-NetIPConfiguration

    Then set the servers with Set-DnsClientServerAddress, replacing 6 with your index:

    Set-DnsClientServerAddress -InterfaceIndex 6 -ServerAddresses 1.1.1.1,1.0.0.1

    To roll back to DHCP-assigned DNS:

    Set-DnsClientServerAddress -InterfaceIndex 6 -ResetServerAddresses

    In Command Prompt (run as administrator), netsh does the same job using the adapter name:

    netsh interface ipv4 set dnsservers name="Wi-Fi" static 1.1.1.1 primary
    netsh interface ipv4 add dnsservers name="Wi-Fi" 1.0.0.1 index=2

    Revert with netsh interface ipv4 set dnsservers name="Wi-Fi" source=dhcp. Adapter names must match exactly, so run netsh interface show interface first if you’re unsure.

    Configure IPv6 and DNS over HTTPS Where Supported

    If your ISP gives you IPv6 connectivity, set IPv6 resolvers too. Otherwise your device keeps asking the ISP’s IPv6 DNS server for some lookups, and your change only half applies. In the Windows 11 Edit DNS settings window, toggle IPv6 on and enter the provider’s IPv6 pair, such as 2606:4700:4700::1111 and 2606:4700:4700::1001 for Cloudflare. In Control Panel, the same fields sit under Internet Protocol Version 6 (TCP/IPv6).

    Windows 11 also supports DNS over HTTPS, which encrypts lookups between your PC and the resolver. After entering a recognized resolver address in Settings, the DNS over HTTPS dropdown appears under each server. Choose On (automatic template) to encrypt queries to providers Windows knows, including Cloudflare, Google, and Quad9. Run netsh dns show encryption to list the resolvers Windows has templates for.

    How Do You Set DNS on Other Devices and Your Router?

    A person configures a laptop beside a Wi-Fi router, smartphone, and tablet.

    Every platform stores a DNS server address per network connection, and each has both a graphical path and, on desktops, a command-line equivalent. Mobile devices add encrypted “Private DNS” options that take a hostname, while routers push your choice to every client.

    Update DNS on macOS

    On macOS Ventura and later:

    1. Open Apple menu > System Settings > Network.
    2. Select Wi-Fi or Ethernet, then click Details next to your connected network.
    3. Choose DNS in the sidebar.
    4. Under DNS Servers, click + and enter your primary address, then click + again for the secondary.
    5. Click OK.

    Gray entries are values your router supplied; your manual entries replace them. From Terminal, the same change is one line:

    networksetup -setdnsservers Wi-Fi 1.1.1.1 1.0.0.1

    To return to DHCP-assigned DNS, run networksetup -setdnsservers Wi-Fi Empty. Use networksetup -listallnetworkservices if your service name differs from “Wi-Fi.”

    Update DNS on Linux

    On desktop distributions using NetworkManager (Ubuntu, Fedora, and most others), open Settings > Wi-Fi or Network, click the gear next to your connection, open the IPv4 tab, turn off Automatic DNS, enter comma-separated addresses, and click Apply. Toggle the connection off and on to load the change.

    From the terminal, nmcli is cleaner and scriptable:

    nmcli connection show --active
    nmcli connection modify "Home-WiFi" ipv4.dns "1.1.1.1 1.0.0.1" ipv4.ignore-auto-dns yes
    nmcli connection up "Home-WiFi"

    Revert with ipv4.dns "" ipv4.ignore-auto-dns no. Avoid editing /etc/resolv.conf directly on systemd-resolved systems; it points to a local stub at 127.0.0.53 and gets rewritten.

    Update DNS on iPhone, iPad, and Android

    On iPhone and iPad, DNS is set per Wi-Fi network:

    1. Open Settings > Wi-Fi and tap the (i) next to your network.
    2. Scroll to Configure DNS and choose Manual.
    3. Delete the existing entries, tap Add Server, and enter your addresses.
    4. Tap Save.

    Cellular connections on iOS don’t expose this setting; you’d need a provider’s configuration profile or app for encrypted DNS on mobile data.

    On Android 9 and later, the cleanest option is Private DNS, which applies to Wi-Fi and mobile data and encrypts lookups with DNS over TLS:

    1. Open Settings > Network & internet (Samsung: Connections > More connection settings).
    2. Tap Private DNS and choose Private DNS provider hostname.
    3. Enter a hostname such as one.one.one.one (Cloudflare) or dns.google (Google).
    4. Tap Save.

    Private DNS takes a hostname, so typing 1.1.1.1 into that field fails.

    Update Your Router for Devices Across the Network

    A router change covers smart TVs, consoles, and guest devices you can’t configure individually. Find your router’s IP address from the Default Gateway line in ipconfig (common values are 192.168.1.1 and 192.168.0.1), sign in with the admin credentials, and look for the DNS fields on the WAN or Internet page. Common locations:

    Router brand Typical path
    TP-Link Advanced > Network > Internet (classic UI: Network > WAN)
    Netgear Advanced > Setup > Internet Setup
    Asus WAN > Internet Connection > WAN DNS Setting
    Linksys Connectivity > Internet Settings
    D-Link Setup > Internet > Manual Internet Connection Setup

    Switch from automatic to manual DNS, enter the primary and secondary addresses, and save. Screenshot the original values first.

    Clients keep their old resolver until their lease renews, a detail that makes more sense once you know what DHCP does on your network. Reboot the router or reconnect each device to force it. ISP-rented gateways from some providers lock these fields; in that case, set DNS on each device or put the gateway in bridge mode behind your own router.

    How Can You Verify the New Resolver Is Working?

    Verification takes three checks: confirm the address your device is configured to use, confirm lookups succeed through that resolver, and confirm nothing else on the system is quietly sending queries elsewhere. Saving a setting proves nothing until you’ve seen the new DNS server answer.

    Check the DNS Addresses Assigned to Your Device

    Each platform reports its active resolvers with one command:

    • Windows: ipconfig /all (look for DNS Servers under your active adapter) or Get-DnsClientServerAddress in PowerShell
    • macOS: scutil --dns | grep nameserver
    • Linux: resolvectl status or nmcli device show | grep DNS
    • iPhone/Android: reopen the Wi-Fi details or Private DNS screen; Android shows “Connected” under Private DNS when the hostname validates

    If you changed the router, your device will still list the router’s own address (such as 192.168.1.1) as its DNS server. That’s normal; the router forwards queries upstream, so check the router’s status page or run the external tests below.

    Test Name Resolution and Compare DNS Results with PacketTools

    Run nslookup packettools.com and read the Server and Address lines at the top. They should show your new resolver. On Windows, nslookup contacts only the primary DNS server configured, so use Resolve-DnsName packettools.com to test what the full Windows client does, including fallback to the alternate.

    Query a resolver directly to compare answers: nslookup packettools.com 1.1.1.1 versus nslookup packettools.com 8.8.8.8. Different IPs aren’t automatically a fault; answers differ during the 24-48 hour propagation window after a record change, and CDN-hosted domains return location-based results.

    For an outside view, the PacketTools DNS Propagation Checker queries public resolvers worldwide, and DNS Lookup checks individual record types. Neither logs your queries. A DNS leak test shows which resolver operator the internet sees your lookups coming from, which catches router or ISP interception your local commands miss.

    Account for Browser Secure DNS, VPNs, and Cached Answers

    Your OS setting can be correct while traffic still goes elsewhere. Three common overrides:

    • Browser secure DNS: Chrome, Edge, and Firefox can send lookups over DNS over HTTPS to their own configured provider. Check Settings > Privacy and security > Use secure DNS in Chrome or Edge, and Privacy & Security > DNS over HTTPS in Firefox.
    • VPN clients: most VPNs push their own resolvers while connected, replacing yours until you disconnect.
    • Cached answers: your OS, browser, and router each cache results until the record’s TTL expires, so an old answer can survive a resolver change.

    Test with the VPN off and in a fresh browser window before deciding the change failed.

    What If Sites Stop Resolving?

    A typo in the DNS server address is the most common reason sites stop loading right after a change, followed by setting DNS on the wrong adapter and network policies that block outside resolvers. Work through those before assuming the provider is down.

    Check the Address, Adapter, and Network Policy

    Start with the configuration you just entered:

    1. Re-read the address. 1.1.1.1 typed as 1.1.11 or 8.8.8.8 entered as 8.8.4 makes every lookup time out. Browser errors like DNS_PROBE_FINISHED_BAD_CONFIG point straight at this.
    2. Confirm the adapter. Machines with Wi-Fi, Ethernet, and virtual adapters (Hyper-V, VMware, VPN) often get the change on an inactive interface. Match the adapter in ipconfig /all to the one carrying your default gateway.
    3. Ping the resolver. ping 1.1.1.1 should reply. If it doesn’t, something between you and the resolver is blocking it.
    4. Check network policy. Corporate networks, schools, and some guest Wi-Fi block outbound UDP and TCP port 53 to anything except their own resolvers. Firewalls and endpoint security products do the same locally.

    On a managed work device, Group Policy or MDM can overwrite your DNS settings at the next refresh. Follow your organization’s policy there. Persistent “DNS server not responding” errors on a clean configuration usually mean the resolver is unreachable from your network.

    Clear Cached Results and Restore the Previous DNS Configuration

    Clear stale answers before retesting. Windows checks the cache, then the Hosts file, then the DNS server when resolving names… that order means a cached or hosts-file entry wins every time.

    To flush the DNS cache:

    • Windows: ipconfig /flushdns
    • macOS: sudo dscacheutil -flushcache; sudo killall -HUP mDNSResponder
    • Linux (systemd-resolved): resolvectl flush-caches
    • Chrome/Edge: visit chrome://net-internals/#dns and click Clear host cache

    If lookups still fail, roll back using the values you recorded. Set Windows back to Automatic (DHCP) or run Set-DnsClientServerAddress -ResetServerAddresses, use networksetup -setdnsservers Wi-Fi Empty on macOS, and set iOS Configure DNS back to Automatic. Restore the router’s original WAN DNS values from your screenshot. Once resolution works again, retry the new resolver on a single device to isolate the fault.

    Choose a Resolver, Test It, and Keep a Way Back

    A clean DNS change follows the same order on every platform: write down the current values, set a matched primary and secondary from one provider, and confirm with nslookup or Resolve-DnsName that the new server answers.

    Test on one device first. Move the change to your router only after that device resolves sites reliably for a day, since a router mistake takes down every client on the network.

    Keep your rollback commands handy:

    • Windows: set Automatic (DHCP) or run Set-DnsClientServerAddress -InterfaceIndex <n> -ResetServerAddresses
    • macOS: networksetup -setdnsservers Wi-Fi Empty
    • Linux: clear ipv4.dns and set ipv4.ignore-auto-dns no
    • Router: re-enter the original WAN DNS values from your screenshot

    When results look odd, check browser secure DNS and any active VPN before blaming the resolver. Then compare answers across public resolvers with the PacketTools DNS Propagation Checker and DNS Lookup, and flush local caches once the outside view looks correct.

  • WHOIS IP Lookup: Find the Network Behind an Address

    WHOIS IP Lookup: Find the Network Behind an Address

    Every public IP address on the internet traces back to a registration record, and that record tells you which organization holds the block it sits in. A WHOIS IP lookup queries the regional internet registry responsible for an address and returns the registered organization, the full IP range, and an abuse contact you can use to report traffic. That is often enough to tell a cloud server from a home broadband connection in under a minute.

    A cybersecurity analyst examines a global network map on a computer.

    PacketTools was built by an engineer with over 28 years in enterprise IT, and the same registration checks described here show up daily when verifying VPN endpoints, chasing odd firewall hits, and confirming who owns a netblock before opening a ticket. The record is useful, but it has limits that trip up even experienced admins.

    Once you can read the fields correctly, you will know when to trust the record, when to cross-check it with DNS and routing data, and where to send an abuse report so it reaches someone who can act.

    How Do You Look Up an IP Address or Domain?

    You run a lookup by sending the address or domain name to a WHOIS or RDAP service, either from a web tool or a terminal. IP queries go to a regional internet registry, while domain queries go to the registry and registrar for that top-level domain, so the two searches return different kinds of records.

    Look Up a Public IPv4 or IPv6 Address

    An ip whois lookup works the same way for IPv4 and IPv6. Paste the address into a web lookup tool, or use the command line:

    • macOS and Linux: whois 8.8.8.8
    • Windows: install a WHOIS client, or use a browser-based RDAP tool
    • Registry web search: enter the address directly into a registry’s search box

    ARIN’s own search auto-detects what you type. Its documentation shows that entering an IPv6 address such as 2001:500:11:: triggers a network query automatically, and that ARIN Whois/RDAP does not accept wildcards in IP or CIDR searches. You can also search a whole CIDR range like 192.0.2.0/24.

    Two practical tips from daily use:

    1. Check that the address is public. Private ranges (10.0.0.0/8, 172.16.0.0/12, 192.168.0.0/16) and CGNAT space return registry placeholder records, which tell you nothing about the device. If you are unsure what your own public address is, confirm it with what is my IP first.
    2. Query IPv6 with the full or compressed form. Both resolve to the same allocation, and IPv6 blocks are far larger, so expect wide ranges such as a /32 assigned to a single provider. The IPv4 vs IPv6 differences explain why those blocks look so big.

    Look Up a Domain and Check Its DNS Records

    A domain whois lookup returns registrar data: creation and expiry dates, the registrar name, status codes, and nameservers. ICANN’s registration data lookup tool covers both domain names and Internet number resources through RDAP.

    Registration data only tells you who manages the name. To see where it points today, resolve the A, AAAA, and MX records, then run a WHOIS lookup on the resulting IPs. That second step reveals the hosting provider or CDN in front of the site.

    For a domain-wide pass, the PacketTools SuperTool runs DNS, MX, SPF, DKIM, DMARC, blacklist, and SSL checks in one go. Pair that with a review of DNS record types if any result looks unfamiliar.

    What Do the Registration Fields Tell You?

    A cybersecurity analyst examines abstract network and location data on computer screens.

    A whois record for an IP describes an organization and its address space, and a domain record describes a name and its registrar. Reading the right fields for each tells you who controls the resource and who to contact about it.

    Read the Organization, IP Range, and Network Contacts

    IP records vary in labeling between registries, but the core fields line up:

    Field (ARIN / RIPE style) What it tells you
    NetRange / inetnum First and last address in the IP block
    CIDR The same IP range in prefix notation
    NetName / netname Short label the holder chose for the network
    Organization / descr The registered holder, showing IP ownership
    OrgAbuseEmail / abuse-mailbox The abuse contact for that range
    RegDate, Updated / created When the record was created and last changed
    Parent / NetType Whether this is a direct allocation or a sub-assignment

    The NetType field deserves attention. A “Direct Allocation” means the registry gave the block straight to that organization. A “Reassigned” or “Reallocated” entry means an ISP or hosting provider carved a smaller block out for a customer, so you may see two nested records.

    The abuse contact is usually the most actionable line. Large providers route those mailboxes into ticketing systems, and a report with timestamps and logs gets handled faster than a vague complaint.

    ARIN states that it publishes only organizational information in its public Whois, including Point of Contact records, and keeps personal profile details confidential. Expect role addresses like noc@ and abuse@, never a named individual’s home address.

    Distinguish Domain Registration Details from IP Records

    Domain records answer a different question. They show the registrar, the creation and expiry dates, status codes such as clientTransferProhibited, and nameserver information that reveals the DNS provider.

    Since GDPR took effect in 2018, registrant names and emails on most domains appear as “REDACTED FOR PRIVACY.” Treat that as normal. The creation date stays visible, and a domain claiming a long history while showing a registration from last month is a strong phishing signal.

    IP records held up better under privacy rules because they describe organizations. One company can hold a single large allocation and run hundreds of domains on it, so a domain’s registrant and the IP’s holder frequently differ.

    Where Does the Data Come From?

    A network researcher examines a visualization of connected servers and data sources.

    IP registration data lives in the whois database of five regional internet registries, which receive address space from IANA and assign it to ISPs and organizations. You can query those databases over the older port 43 protocol or the newer RDAP, and the underlying records are the same.

    Understand the Five Regional Internet Registries

    Each RIR manages internet number resources (IP addresses and ASNs) for its region and sets its own allocation policies:

    RIR Region WHOIS server
    ARIN United States, Canada, parts of the Caribbean whois.arin.net
    RIPE NCC Europe, Middle East, Central Asia whois.ripe.net
    APNIC Asia-Pacific whois.apnic.net
    LACNIC Latin America and the Caribbean whois.lacnic.net
    AFRINIC Africa whois.afrinic.net

    Most web tools follow referrals automatically, so you rarely need to know the right registry in advance. When querying by hand, a result from ARIN that says “transferred to RIPE” or points you elsewhere means you should repeat the query on the listed server.

    Legacy blocks add a wrinkle. Addresses assigned before the RIR system existed, and blocks moved between regions through inter-RIR transfers, can sit in a registry that does not match where the holder operates.

    Compare Traditional WHOIS with RDAP

    WHOIS is a query and response protocol for databases of registered users of resources such as domain names, IP blocks, and autonomous systems. It runs on TCP port 43, defined in RFC 3912, and returns free-form text that varies by registry.

    RDAP (Registration Data Access Protocol, RFC 7480 and related standards) was developed with IETF guidance as its replacement. Key differences:

    Traditional WHOIS RDAP
    Transport TCP port 43 HTTPS
    Output Unstructured text Structured JSON
    Format consistency Differs per registry Standardized fields
    Authentication None Supported
    Referrals Manual or tool-specific Built-in bootstrap and links

    ARIN began building RDAP support after the protocol emerged in 2015, added a web interface in 2019, and made Whois/RDAP its featured service that year while still supporting Whois-RWS. ICANN’s lookup tool also runs on RDAP. For scripts and SIEM enrichment, RDAP’s JSON saves you from writing a parser for every registry’s text layout.

    What Can an IP Lookup Not Prove?

    A registration record identifies the network holder and nothing more. It cannot name the person behind a connection, prove where a device sits, or confirm who sent a specific packet.

    Why the Registered Holder May Not Be the End User

    The organization in the record is whoever the registry assigned the block to. On cloud platforms, that is the provider (AWS, Microsoft, DigitalOcean) even though thousands of customers rent virtual machines on those addresses.

    Residential addresses resolve to the ISP. With carrier-grade NAT, many subscribers share one public IPv4 address at the same moment, and only the ISP’s logs can map a timestamp and port to a subscriber. VPN exit nodes and proxy services produce the same effect: the record names the VPN operator.

    Treat the holder as the party responsible for the network, and the abuse contact as the route to whoever controls the specific machine.

    Why Location, Routing, and Contact Data May Differ

    The country field shows where the holder registered, which frequently differs from where traffic originates. A US company can announce its ARIN block from data centers in Frankfurt or Singapore.

    IP geolocation databases estimate location separately, using routing, latency, and submitted data, so their city-level guesses can disagree with the registry record and with each other.

    Routing is another layer. The autonomous system number (ASN) announcing a prefix in BGP may belong to a different operator than the registered holder, for example when a customer’s block is routed through its upstream provider. Contacts drift too: records with old update dates point to mailboxes nobody reads, so check the “Updated” field before relying on an email address.

    How Can You Use the Results in Network Troubleshooting?

    Registration data works best as one input alongside DNS and path checks. Combined, they tell you what an address is, who to call, and whether the problem sits on your side or theirs.

    Investigate an Unfamiliar Address or Report Abuse

    When an unknown IP shows up in firewall logs or connection tables, work through it in order:

    1. Look up the registration. Note the holder, NetType, and range.
    2. Run reverse DNS. A PTR such as ec2-...compute.amazonaws.com or a hostname with “dsl” or “cable” in it tells you server versus residential quickly.
    3. Check whether your own systems use it. SaaS and Microsoft 365 traffic often hits ranges you do not recognize; the M365 domain checker helps confirm tenant-related DNS.
    4. Report with evidence. Send the abuse contact UTC timestamps, destination ports, and log excerpts. Hosting providers act on specific, reproducible reports.

    If the range is large, block the specific prefix from the record. An IP subnet calculator turns a start and end address into clean CIDR entries for your firewall.

    Correlate Registration Data with DNS and Route Checks

    Mismatches between data sources point to real problems. If a domain’s A record lands on a provider you did not expect, you may be looking at stale DNS, a hijacked record, or an unfinished migration. The DNS propagation checker shows whether resolvers worldwide agree.

    For latency or reachability complaints, run a traceroute and look up the IPs of the hops where delay jumps or replies stop. That identifies which carrier owns the bad segment, and the guide on how to trace a route covers reading those hops. Add a ping test to measure loss before you escalate to that carrier’s NOC.

    Use Registration Data as a Starting Point

    A registration lookup gives you the holder of an IP block, its range, and an abuse contact, pulled from one of five RIRs over WHOIS or RDAP. Domain records add registrar dates and nameservers, though personal registrant details are now mostly redacted.

    Keep the limits in view. The holder may be a cloud provider or ISP far removed from the actual user, the country field reflects registration, and contacts on stale records go unanswered.

    Pair each lookup with reverse DNS, current DNS resolution, and a traceroute before you block a range or file a report. When the record’s “Updated” date is years old, confirm the contact through the provider’s own abuse page before sending evidence.

  • DNS Record Types Explained for Network Troubleshooting

    DNS Record Types Explained for Network Troubleshooting

    Every outage ticket that says “the site is down” or “mail is bouncing” eventually becomes a question about one record in one zone. The DNS record types that matter most for troubleshooting are A and AAAA (website addresses), CNAME (aliases), MX and TXT (mail routing and authentication), PTR (reverse DNS), NS and SOA (delegation and authority), and CAA plus the DNSSEC set (certificate and integrity controls). When you know which record answers which question, you can stop guessing and query the exact record behind the failure.

    A server connected by glowing network paths to several destination icons.

    PacketTools was built by an engineer with over 28 years of production IT experience, and the same lookups described below are the ones used to verify VPNs, analyze routing, and harden infrastructure. By the end, you will be able to read a DNS answer field by field, tell a stale cache from a broken zone, and match a symptom to the record that causes it.

    Which Records Connect Domain Names to Websites?

    A computer, server, and globe connected by network pathways.

    Three record types get a browser from a domain name to a server: A records hold IPv4 addresses, AAAA records hold IPv6 addresses, and CNAME records point one name at another name. The apex of a zone adds a wrinkle, because the bare domain can’t hold a standard CNAME, so providers solve it with flattening.

    How Do A and AAAA Records Point to IPv4 and IPv6 Addresses?

    An A record maps a hostname to a 32-bit IPv4 address. An AAAA record (“quad-A”) does the same job for a 128-bit IPv6 address. If the difference between the two address families is fuzzy, the IPv4 vs IPv6 breakdown covers it.

    A typical pair in a zone file looks like this:

    www.example.com.  3600  IN  A     198.51.100.10
    www.example.com.  3600  IN  AAAA  2001:db8::10

    A few field-tested points:

    • Multiple A records on one name spread traffic across servers in round-robin fashion. That is crude load balancing with no health checks, so a dead server keeps receiving its share.
    • Publish AAAA only when the server listens on IPv6. Dual-stack clients prefer the AAAA answer, and a dead IPv6 address produces slow page loads that look like a network problem.
    • Address records hold the IP literally. Migrate a server and every A record pointing at the old address has to change.

    Naming limits apply too. DNS labels are capped at 63 characters and a fully qualified name at 253, which occasionally bites automated subdomain generators.

    When Should You Use a CNAME Instead of an Address Record?

    Use a CNAME record when you want a subdomain to follow a hostname you don’t control, such as a SaaS platform, a CDN configuration, or a load balancing endpoint whose IPs rotate. The resolver hits the CNAME, restarts the lookup against the canonical name, and returns whatever that target resolves to.

    www.example.com.  3600  IN  CNAME  webhost.example.net.

    Two rules cause most CNAME tickets you will see:

    1. A CNAME must stand alone. No A, MX, or TXT record can exist at the same name.
    2. The target must be a hostname. A CNAME never points at an IP address.

    Chains are legal, but each hop adds a lookup and another place to break. When a subdomain resolves inconsistently, query the CNAME and then query the target separately to find which hop is stale.

    What Happens When a CNAME Is Needed at the Zone Apex?

    The bare domain (example.com) already carries mandatory SOA and NS records, so a standard CNAME there would violate the stand-alone rule. Yet hosting platforms and CDNs often hand you a hostname, not an IP, for the root domain.

    Providers solve this with CNAME flattening, sometimes sold as ALIAS or ANAME. The authoritative server resolves the target itself and serves the resulting A and AAAA records at the apex. Resolvers never see a CNAME.

    The troubleshooting consequence: a dig example.com CNAME returns nothing even though your dashboard shows one. Query A and AAAA instead, and compare the returned IPs with what the target hostname resolves to directly. A mismatch points to the provider’s flattening cache lagging behind a change at the target.

    Which Records Route and Authenticate Email?

    Mail depends on MX records to find the receiving server, TXT records to publish SPF, DKIM, and DMARC policy, and PTR records to prove a sending IP’s identity. A fault in any one of them produces bounces or spam-folder placement with no error on the website side.

    How Do MX Priorities Direct Incoming Mail?

    An MX record pairs a priority number with a mail server hostname. Sending servers try the lowest number first and fall back to higher numbers when the preferred host refuses or times out over SMTP. Equal priorities share the load.

    example.com.  3600  IN  MX  10  mail1.example.com.
    example.com.  3600  IN  MX  20  mail2.example.com.

    Checks to run when inbound email delivery fails:

    • Confirm the MX target has its own A or AAAA record. An MX pointing at a CNAME or a bare IP breaks the spec, and some senders reject it outright.
    • Copy provider values exactly. Microsoft 365 tenants use a hostname ending in mail.protection.outlook.com; a typo there silently misroutes everything.
    • Watch the backup MX. A low-preference server that accepts mail but never forwards it is a classic cause of “some messages vanish.”

    What Do TXT Records Publish for SPF, DKIM, DMARC, and Verification?

    TXT records carry free-form text that specific systems read as configuration. For email authentication, that means three records in three locations:

    Record Location Purpose
    SPF Root of the domain Lists IPs and services allowed to send as you
    DKIM selector._domainkey subdomain Publishes the public key for signature checks
    DMARC _dmarc subdomain Tells receivers what to do when SPF and DKIM fail

    The SPF failure you will hit most often is the lookup cap. RFC 7208 limits SPF evaluation to 10 DNS lookups, and every include: counts, so a domain using several email platforms exceeds it fast and returns a permerror. Domains are also allowed only one SPF record; two v=spf1 strings break both.

    DKIM keys at 2048 bits exceed the 255-character limit of a single TXT string, so they are split into quoted chunks that resolvers concatenate. A missing quote in a pasted key is a common silent failure.

    Domain verification tokens for services like Microsoft 365 live here too. They accumulate over the years; prune ones tied to services you no longer use.

    Why Does a Sending Server Need Reverse DNS?

    A PTR record maps an IP address back to a hostname, the reverse of an A record. Receiving mail servers run a reverse DNS lookup on the connecting IP, and many reject or score down mail from IPs with no PTR or with a generic ISP-style name.

    Good practice is forward-confirmed reverse DNS: the PTR for 203.0.113.10 returns mail.example.com, and the A record for mail.example.com returns 203.0.113.10.

    PTR records live in the reverse zone controlled by whoever owns the IP block, so you set them in your hosting or VPS provider’s panel, not your domain’s zone. If you send through a hosted platform, the provider manages PTR for its own IPs.

    How Do Delegation and Service Discovery Work?

    A network engineer views connected servers and data pathways in a data center.

    NS and SOA records decide which servers are authoritative for a zone and how copies stay in sync. SRV, NAPTR, and HTTPS records tell clients where an application service lives, and HINFO survives mostly as a curiosity.

    How Do NS and SOA Records Define Authority for a Zone?

    NS records name the authoritative nameservers for a DNS zone. They appear twice: in the parent zone (the TLD), where they perform DNS delegation, and at your apex, where your own servers declare themselves. Those two sets should match. When they diverge, resolvers follow the parent’s delegation while tools read the child’s, and you get inconsistent answers that are hard to reproduce.

    When a nameserver lives inside the domain it serves (ns1.example.com for example.com), the parent must also publish its IP as a glue record. Most TLD registries require at least two nameservers, ideally on separate networks.

    The SOA record (start of authority) appears once per zone and holds:

    • The primary nameserver and responsible contact
    • A serial number that secondaries compare before pulling a zone transfer
    • Refresh, retry, and expire timers
    • The negative caching TTL, the last field, which controls how long resolvers remember that a name does not exist

    A serial that differs between authoritative nameservers tells you a secondary failed to sync.

    How Do SRV and NAPTR Records Locate Application Services?

    An SRV record gives a service location as priority, weight, port, and target host. Names follow a _service._protocol pattern:

    _sip._tcp.example.com.  3600  IN  SRV  10 60 5060 sipserver.example.com.

    SIP and VoIP phones, XMPP chat servers, LDAP clients, and Active Directory domain controllers all rely on SRV lookups. If a softphone registers on one network but not another, query the SRV record from both; split DNS serving a different answer internally is a frequent culprit.

    A NAPTR record adds a rewrite step, translating a name or phone number into a URI or another lookup, and it sits upstream of SRV in many telephony stacks (ENUM being the classic case). You will mostly meet NAPTR in carrier SIP trunking setups.

    What Are HTTPS and HINFO Records Used For?

    HTTPS records (a variant of the SVCB type) let a domain advertise connection parameters before the client connects: supported protocols such as HTTP/3, alternative endpoints, and IP hints. Unlike a CNAME, an HTTPS record works at the apex, which gives it a role in aliasing the bare domain. If clients connect over HTTP/3 to some hosts and fail over to TCP on others, check whether an HTTPS record advertises h3 on an endpoint that doesn’t support it.

    HINFO records describe host CPU and operating system. Publishing that publicly hands attackers reconnaissance, so treat HINFO as legacy. You will still see it occasionally, because some servers return HINFO as a minimal reply to ANY queries.

    Which Records Support DNS and Certificate Security?

    CAA records control which certificate authorities can issue SSL/TLS certificates for your names, DNSSEC records let resolvers verify that answers weren’t forged, and DANE ties TLS keys directly to DNSSEC-signed data. Each one adds a failure mode you need to recognize.

    How Do CAA Records Restrict Certificate Issuance?

    A CAA record (certificate authority authorization) lists the CAs allowed to issue for a domain. Public CAs must check it before issuing.

    example.com.  3600  IN  CAA  0 issue "letsencrypt.org"
    example.com.  3600  IN  CAA  0 issuewild ";"
    example.com.  3600  IN  CAA  0 iodef "mailto:security@example.com"

    The second line blocks all wildcard issuance; the third requests reports of violations.

    The troubleshooting pattern: certificate renewals suddenly fail after someone adds CAA for one vendor, and an automated tool using a different CA gets refused. CAA lookups also climb the tree, so a record on example.com governs shop.example.com unless the subdomain publishes its own. When issuance fails with a CAA error, query CAA on the exact name and every parent up to the apex.

    How Do DNSKEY, DS, RRSIG, NSEC, and NSEC3 Support DNSSEC?

    DNSSEC builds a chain of trust from the root down to your zone using five record types:

    Record Role
    DNSKEY Public keys for the zone (key-signing and zone-signing)
    DS Hash of your key-signing key, published in the parent zone
    RRSIG Signature over each set of records
    NSEC Signed proof that a name or type does not exist
    NSEC3 Same proof using hashed names to hinder zone walking

    Most DNSSEC outages come from a broken link between DS and DNSKEY: you change DNS providers or roll keys, and the DS at the registrar still references the old key. Validating resolvers then return SERVFAIL for the whole domain, while non-validating resolvers answer normally. That split is the signature you’re looking for.

    Expired RRSIG signatures produce the same symptom. Run dig +dnssec and check the signature expiration timestamps.

    Where Does DANE Fit in TLS Authentication?

    DNS-based Authentication of Named Entities (DANE) publishes TLSA records containing a certificate or public key hash, so a client can confirm the server’s TLS key using DNSSEC-validated data. Its biggest real-world use is SMTP between mail servers, where it protects opportunistic TLS against downgrade attacks.

    DANE only works on a DNSSEC-signed zone. The operational trap is certificate rotation: replace a mail server’s certificate without updating the TLSA record first, and DANE-enforcing senders refuse delivery. Publish the new hash alongside the old one, wait out the TTL, and then swap certificates.

    How Can You Read and Troubleshoot DNS Answers?

    Every DNS answer has the same five fields, and comparing what a resolver returns against what the authoritative server holds separates caching delays from zone errors. With those two skills, a symptom narrows to one record in minutes.

    What Do the Name, TTL, Class, Type, and Value Mean?

    Every line in a DNS zone file or lookup output reads left to right the same way:

    example.com.   3600   IN   A   93.184.216.34
    • Name: the owner of the record. The trailing dot marks it fully qualified; forgetting that dot in a raw zone file appends the zone name and creates www.example.com.example.com.
    • TTL: seconds a DNS resolver may cache the answer. Repeated queries to a resolver show it counting down, proof you’re seeing a cached copy.
    • Class: almost always IN for Internet.
    • Type: A, MX, TXT, and so on.
    • Value: type-specific data, such as an IP, a priority plus host, or quoted text.

    The header matters as much as the record. A status of SERVFAIL often signals a DNSSEC validation failure or broken delegation, while NXDOMAIN means the name does not exist. NOERROR with an empty answer section means the name exists but has no record of that type. The aa flag confirms you reached an authoritative server.

    How Do You Compare Resolver Answers with Authoritative Records?

    Query three places and compare the results:

    1. Your local resolver: dig example.com A
    2. Public resolvers: dig @8.8.8.8 example.com A and dig @1.1.1.1 example.com A
    3. The authoritative server directly: dig @ns1.example.com example.com A

    Interpret the pattern:

    Result Meaning
    Authoritative wrong Zone error; fix the record
    Authoritative right, public resolvers mixed Normal propagation; wait out the TTL
    Only your machine wrong Local cache; flush the DNS cache
    Authoritative servers disagree Secondary out of sync; compare SOA serials

    Negative answers persist too. The last number in the SOA record sets the negative cache TTL, and no one can force a third-party resolver to drop a cached NXDOMAIN before it expires. A DNS propagation checker shows the same comparison across many resolvers worldwide at once.

    Before planned changes, lower the TTL to around 300 seconds, wait for the old TTL to expire, then make the edit. Mistakes then clear in minutes.

    Which Checks Help Isolate Website, Email, and Delegation Failures?

    Map the symptom to the smallest set of queries:

    Website won’t load or loads the wrong site

    • Query A and AAAA; confirm both IPs serve the site
    • Follow any CNAME chain hop by hop
    • If the browser shows a config error, the DNS probe finished bad config walkthrough covers client-side causes

    Mail bouncing or landing in spam

    • Query MX, then the A record of each MX target
    • Read the SPF, DMARC, and DKIM selector TXT records
    • Check PTR on your sending IP
    • The PacketTools SuperTool runs DNS, MX, SPF, DKIM, DMARC, blacklist, and SSL checks in one pass

    Whole domain unreachable

    • Run dig +trace example.com to watch each delegation step
    • Compare NS at the TLD with NS at your apex
    • Check DS against DNSKEY if the zone is signed

    For broader client-side failures, the guides on troubleshooting DNS issues and a DNS server not responding pick up where record checks end.

    Choose the Record That Matches the Failure

    Start every DNS investigation with the symptom, and let it point you to one record family:

    Symptom Records to query first
    Site unreachable or wrong server A, AAAA, CNAME
    Root domain broken on a CDN Flattened A/AAAA at the apex
    Inbound mail missing MX and the MX target’s A record
    Outbound mail rejected or spammed SPF, DKIM, DMARC TXT; PTR
    VoIP or directory clients failing SRV, NAPTR
    Certificate issuance refused CAA up the tree
    SERVFAIL on validating resolvers only DS, DNSKEY, RRSIG
    Every record failing NS at parent and child, SOA serials

    Then read each answer field by field: status code, aa flag, TTL, and value. Query the authoritative server before blaming propagation, and check public resolvers before blaming the zone. If the authoritative answer is correct and only caches disagree, the fix is time; if the authoritative answer is wrong, the fix is a zone edit, made after you’ve lowered the TTL so any correction spreads within minutes.

  • DHCP vs. Static IP: Which Address Setup Should You Use?

    DHCP vs. Static IP: Which Address Setup Should You Use?

    Every device on your network needs an address, and you get to decide whether a server hands it out automatically or you type it in yourself. Pick wrong and you get printers that vanish from the print dialog, port forwards that stop working after a reboot, or two machines fighting over the same address.

    A router connects several devices, with flowing light paths on one side and a steady path to a single device on the other.

    Use DHCP for laptops, phones, and most other clients, and give a fixed address (a DHCP reservation or a manual static IP) only to devices other systems must find at a known location, such as printers, NAS boxes, servers, and your router. That split keeps administration light while making the devices you depend on predictable.

    PacketTools builds its guidance from nearly three decades of production IT work, and the same reasoning applies whether you run a home Wi-Fi network or a business network with hundreds of hosts. By the end, you will be able to place each device in the right category and diagnose the address problems that come up when the plan breaks.

    What Changes When You Choose DHCP or a Static IP?

    A router connects a laptop and smartphone, with visual cues showing automatic and fixed network connections.

    Choosing DHCP or a static IP changes who assigns the address, how long it lasts, and what breaks when something fails. DHCP leases addresses from a central server and prevents duplicates, while a static IP address stays fixed until you change it and keeps working with no server involved.

    How Do Assignment, Stability, and Admin Effort Compare?

    With DHCP, IP address assignment is automatic. The server hands the client an address, subnet mask, gateway, and DNS servers as a lease. With a static IP, you enter every value by hand on the device and track it yourself.

    That tracking is the hidden cost. Static addressing has no built-in conflict detection, so administrators must track assignments manually to avoid duplicates. For a few devices that is fine. For fifty, you need a spreadsheet or an IPAM tool, and the spreadsheet drifts.

    Criteria DHCP (dynamic) Static IP (manual)
    Who assigns DHCP server You, per device
    Address stability Stable per lease, can change Fixed until edited
    Admin effort Low High at scale
    Conflict protection Built in None
    Needs DHCP server Yes No
    Best fit Clients, guests, IoT Routers, core servers

    Does a DHCP Address Change Every Time a Device Reconnects?

    No. A dynamic IP address is assigned dynamically, but it rarely moves in practice. When a client reconnects, it asks for its previous address, and the server hands it back if the DHCP lease is still on record.

    Changes happen when a device stays offline past the lease time or when the pool runs short and the address goes to someone else. Some consumer routers also forget their lease table on a power cycle, which is why a laptop that sat in a drawer over a long weekend comes back with a new address.

    If you need to see what a machine currently holds, a quick look at your IP address basics and the ipconfig /all output will show whether DHCP is enabled and when the lease expires.

    What Happens to Each Setup When the DHCP Server Is Unavailable?

    A static device keeps running because it never talks to the DHCP server. DHCP clients with an active lease keep working too, until renewal time arrives.

    New devices and clients whose lease expires during the outage fail to get an address. On Windows and most other systems, they fall back to a self-assigned 169.254.x.x address, which cannot reach the gateway. When you see that range, read it as “no lease received” before you start blaming cabling or Wi-Fi.

    How Does Each Addressing Method Work?

    A technician connects computers to a router and network switch.

    Dynamic Host Configuration Protocol (DHCP) runs a four-message exchange that hands a client its full IP configuration, while manual IP configuration requires you to enter those same values yourself. IPv4 follows this model closely; IPv6 adds a second automatic method on top.

    How Do DHCP Discover, Offer, Request, and Acknowledgment Assign an Address?

    The DHCP server manages a DHCP pool (Microsoft calls the configured range a DHCP scope) and responds to client broadcasts. The exchange runs like this:

    1. DHCP Discover: the client, with no address yet, broadcasts a request looking for any server.
    2. DHCP Offer: a server replies with an available address, subnet mask, and lease duration.
    3. DHCP Request: the client picks one offer and broadcasts its acceptance, so other servers withdraw theirs.
    4. DHCP Acknowledgment: the chosen server confirms the lease and can include the default gateway and DNS servers.

    When multiple DHCP servers answer, the client may receive several offers and accepts the first one it processes. That detail is why a rogue server on your LAN causes so much trouble. For a fuller walkthrough of the protocol itself, see the PacketTools explanation of DHCP meaning.

    What Must You Enter for a Manual Static IP?

    A manual static IP needs four values, and each must match the subnet the device lives on:

    • IP address: unused, inside the subnet, and outside the DHCP pool.
    • Subnet mask: the same mask the router uses, such as 255.255.255.0.
    • Default gateway: your router IP address on the LAN side.
    • DNS servers: the router, an internal DNS server, or a public resolver.

    A single typo here isolates the device. A common exam scenario describes a laptop set to 192.168.2.50 on an office using 192.168.1.x, which cannot reach local resources. You will see the same thing in the field after someone “fixes” a laptop at home and carries it back to work.

    Do the Same Rules Apply to IPv4 and IPv6?

    The principles carry over, but IPv6 changes the mechanics. On IPv6 networks, hosts commonly build their own addresses through SLAAC from router advertisements, and DHCPv6 can supply addresses, DNS, or both depending on how the router flags are set.

    Every IPv6 interface also holds a link-local fe80:: address automatically, so seeing one tells you little about upstream connectivity. Static IPv6 addresses still make sense for routers and servers, though DNS names matter more because the addresses are long. The IPv4 vs IPv6 guide covers the addressing differences in more depth.

    Which Devices Actually Need a Fixed Address?

    Devices need a fixed address when other systems connect to them; devices that only connect outward do fine on DHCP. Sorting your network devices by that one question settles most cases, and it also clears up confusion between your local addresses and the public address your provider assigns.

    Use DHCP for Everyday Clients and Changing Wi-Fi Networks

    Laptops, phones, tablets, smart TVs, and most IoT devices belong on DHCP. They initiate their own connections, so nobody needs to find them at a fixed location.

    Mobile clients also move between networks constantly. A phone with a hand-typed address for your home Wi-Fi network will fail on the coffee shop’s network and at the office. Leave guest networks and BYOD segments fully dynamic, and shorten lease times there so departed visitors free up addresses quickly.

    Keep Printers, NAS Devices, and Hosted Services Reachable

    Give a stable address to anything that serves others:

    • Network printers: drivers and print queues often point at an IP, so an address change breaks printing for everyone.
    • NAS and Plex Media Server hosts: mapped drives, backup jobs, and client apps expect a consistent target.
    • Security cameras and NVRs: recorders pull streams from specific addresses.
    • Web server, email server, FTP server, and other hosting servers: firewall rules and port forwards reference them.
    • VoIP gear and VPN endpoints: phones and remote access tunnels need predictable peers.

    A reservation covers most of these with less effort than manual entry, which the next section explains.

    Separate Local Addressing from a Public IP Supplied by Your ISP

    Your LAN addresses and your public IP are two different things. Your router uses NAT to share one public address from your internet service provider among all your private 192.168.x.x or 10.x.x.x devices.

    Giving your NAS 192.168.1.10 does nothing to your public address. A static public IP is usually a paid, separately configured service used for hosting or inbound remote access. If you only need outside access occasionally, dynamic DNS paired with port forwarding to a fixed LAN address handles it. You can confirm what the internet sees with PacketTools What Is My IP.

    Does a Static IP Help Gaming or Network Performance?

    A static IP has no effect on speed, latency, or general network performance. The address only identifies the device; it does not change the path packets take or the bandwidth available.

    Where a static IP for gaming helps is reachability. If you run a game server or need open NAT on a console, the router’s port forwarding rules must point to a fixed LAN address, and a reservation keeps that rule valid. If the router supports UPnP, consoles open ports themselves and the fixed address matters less. For lag complaints, measure latency and jitter with a ping test before touching address settings.

    When Is a DHCP Reservation the Better Middle Ground?

    A DHCP reservation (some routers call it static DHCP) is the right choice for most devices that need a fixed address. You get a predictable address while all IP management stays in one place on the router or DHCP server.

    How Does a MAC-Based Reservation Keep an Address Stable?

    A reservation ties an address to the device’s MAC address on the DHCP server. The device still runs the normal discover, offer, request, and acknowledgment exchange, but the server always offers the same address.

    In practice this beats static IP assignment on the device for several reasons:

    • Changing the gateway or DNS server later means editing one server, not walking to every device.
    • The address survives an OS reinstall or factory reset of a printer.
    • Conflict protection still works because the server knows the address is taken.
    • Your documentation lives in the router’s reservation list.

    Watch for one trap: phones and newer laptops randomize their MAC per network by default. Disable private MAC for that specific network before you reserve, or the reservation never matches.

    When Should Infrastructure Use a Manually Assigned Address Instead?

    Manually assign addresses to anything that must be up before DHCP exists or that DHCP itself depends on. That covers the router or gateway, the DHCP server, internal DNS servers, domain controllers, switches, and hypervisor management interfaces.

    If those components relied on reservations, a DHCP outage would take down the very services needed to recover. In a business environment, add DHCP failover with synchronized lease data so clients keep renewing if one server goes offline. Keep this manual tier small and documented, and reserve everything else.

    How Do You Configure and Troubleshoot Either Setup?

    Most address problems trace back to overlapping ranges or a wrong gateway or DNS entry, so plan your subnet first and verify the basics before chasing deeper faults. Security comes from controlling who can hand out addresses, and a fixed address adds none.

    Plan the DHCP Pool and Static Range to Avoid IP Conflicts

    Split each subnet into clear blocks before you assign anything. On a /24 home or small office network, a layout like this works:

    • .1: router or gateway
    • .2 to .49: manual static infrastructure and servers
    • .50 to .99: reservations, if your router allows them inside or outside the pool
    • .100 to .250: dynamic DHCP pool

    The rule that prevents most IP conflicts: never type a static address that falls inside the dynamic pool. If you do, the router will eventually lease it to another device. Modern systems detect duplicates and only the first machine to claim the address keeps working, while the second stops communicating. Size the pool for peak device count plus guests so IP address allocation never runs dry.

    Check the Address, Gateway, and DNS Before Blaming Connectivity

    When a device “has Wi-Fi but no internet,” run through these checks in order:

    1. Run ipconfig /all (Windows) or ip addr (Linux). A 169.254.x.x address means no lease arrived.
    2. Confirm the subnet matches your network and the gateway is your router.
    3. Ping the gateway. Failure points to the local link or a wrong static entry.
    4. Ping a public IP such as 1.1.1.1. Success there with failing names points at DNS.
    5. Run ipconfig /release and /renew to force a fresh DHCP exchange.

    If step 4 passes and names still fail, the DNS server not responding guide picks up from there. The broader wifi connected but no internet walkthrough covers the remaining cases.

    Verify Public Reachability with PacketTools Diagnostics

    Once your LAN addressing is right, confirm what the outside world sees. PacketTools runs these tests in your browser with no sign-in, and no IPs, queries, or test data are logged or stored.

    Start with your public address to confirm whether it changed and to check geolocation. Then use the ping and traceroute tools to see whether your hosted service answers and where the path breaks, and DNS Lookup to confirm your dynamic DNS record points at the current IP. For a full domain check, SuperTool runs DNS, MX, SPF, DKIM, DMARC, blacklist, and SSL tests in one pass, which helps when a self-hosted email server sits behind your public address.

    Protect Address Assignment Without Treating Static IPs as a Security Feature

    A static IP does not make a device safer. Attackers scan whole subnets, so a fixed address hides nothing, and IP-based firewall rules only hold if you control who can claim that IP.

    Protect address assignment itself:

    • Enable DHCP snooping on managed switches so only trusted ports can send DHCP offers, which blocks a rogue DHCP server.
    • Pair snooping with dynamic ARP inspection to stop spoofed address claims.
    • Restrict admin access to the DHCP server and router.
    • Review lease logs, since they show which device held an address at a given time during an incident.

    Write firewall rules against reserved or static addresses, and treat them as one layer of network security alongside authentication.

    Use DHCP by Default and Fix Addresses Where Reachability Matters

    Leave clients on DHCP and fix addresses only for devices others must find. Laptops, phones, guest devices, and IoT gear gain nothing from a hand-typed address and lose portability.

    For printers, NAS units, cameras, game consoles with port forwards, and hosted services, a DHCP reservation gives you a stable address while keeping changes centralized. Save manual static configuration for the bootstrap tier: the router, DHCP and DNS servers, switches, and domain controllers.

    Keep the static block outside the dynamic pool, remember that a public static IP is a separate ISP service, and when something breaks, check for a 169.254 address, the gateway, and DNS in that order.

  • Update Network Drivers in Windows 11 and 10

    Update Network Drivers in Windows 11 and 10

    Most Wi-Fi and Ethernet problems that show up after a Windows upgrade, a sleep/resume cycle, or a new router trace back to the software layer between Windows and your adapter. Outdated or mismatched network drivers cause dropped connections, adapters that vanish from the taskbar, and slow internet speeds that no amount of router rebooting will fix.

    An IT professional connects an Ethernet cable to a laptop beside networking equipment.

    The safest way to update network drivers is through Windows Update’s Optional updates page. If that offers nothing, download the driver from your PC or adapter manufacturer and install it through Device Manager. Both methods use signed, vendor-supplied packages, so you avoid the bundled junk that comes with generic driver sites.

    PacketTools is built by an engineer with over 28 years of hands-on experience in enterprise IT and network engineering. The steps below are the same sequence used on production machines: identify the exact adapter, update it from a trusted channel, then prove the fix with real diagnostics. By the end, you will know which driver you have, how to replace it even with no internet, and how to tell whether the driver was ever the problem.

    Which Network Adapter Should You Update?

    An IT professional examines a laptop, computer, and wireless router.

    You should update the adapter you use to connect: the Wi-Fi driver if you’re on wireless, the Ethernet driver if you’re plugged in. Most laptops have both, plus virtual adapters from VPN clients and Hyper-V, so a few minutes of identification keeps you from installing the wrong package and saves a rollback later.

    Find Your Wi-Fi or Ethernet Adapter in Device Manager

    Right-click the Start button and choose Device Manager, then expand Network adapters. You’ll see several entries. The ones that matter are named after real hardware, such as:

    • Wi-Fi: names containing “Wireless,” “Wi-Fi,” “AX,” or “WLAN,” for example Intel(R) Wi-Fi 6 AX201 160MHz or Realtek RTL8852BE WiFi 6 802.11ax PCIe Adapter.
    • Ethernet: names containing “Ethernet,” “GbE,” or “PCIe GbE Family Controller,” such as Intel(R) Ethernet Connection I219-V or Realtek PCIe 2.5GbE Family Controller.
    • Ignore for now: WAN Miniport entries, Bluetooth Device (Personal Area Network), Hyper-V Virtual Ethernet Adapter, and VPN TAP/TUN adapters.

    A yellow triangle on an entry means Windows has a problem with that device. An entry listed under Other devices as “Network Controller” or “Ethernet Controller” means no driver is installed at all, and Windows can’t name the hardware.

    For the full PC make and model, press Win + R, type msinfo32, and press Enter. The System Information window lists System Manufacturer and System Model. Write both down; you’ll need them on the manufacturer’s support site.

    Check the Driver Version and Create a Restore Point

    Double-click your adapter, open the Driver tab, and note the Driver Provider, Driver Date, and Driver Version. For Wi-Fi, running netsh wlan show drivers in Command Prompt gives the same details plus the radio types the adapter supports.

    That version number is your baseline. Without it, you can’t confirm later that anything changed.

    Before you touch the driver, create a system restore point:

    1. Search the Start menu for Create a restore point and open it.
    2. Select your system drive (usually C:) and click Configure if protection is off, then turn it on.
    3. Click Create, give it a name like “Before network driver update,” and confirm.

    Device Manager’s Roll Back Driver button covers most bad updates, but it only keeps one previous version. A restore point protects you when a manufacturer installer also replaces utilities or services.

    Choose a Method Based on Your Connection

    Your current connection state decides which method to start with:

    Your situation Best starting method
    Internet works, problem is drops or slowness Windows Update optional drivers
    Internet works, Windows Update offers nothing Manufacturer download via Device Manager
    Wi-Fi is dead but Ethernet works (or vice versa) Use the working link to download the driver for the broken one
    No internet on this PC at all Download on another computer, move it with a USB drive
    Problem started right after a driver update Roll back first, update second

    If your Wi-Fi shows connected but pages won’t load, read up on WiFi connected but no internet before replacing drivers. That symptom is frequently DNS or IP configuration.

    How Do You Install a Driver Through Windows Update?

    A person uses a desktop computer beside a Wi-Fi router.

    Windows Update installs recommended drivers on its own, but network driver updates frequently sit in the optional section where you have to approve them manually. Windows 11 and Windows 10 put that section in different places, and Windows 11 adds one setting that must be switched on first.

    Check for Automatic and Optional Driver Updates in Windows 11

    Windows 11 installs recommended drivers automatically, and optional drivers aren’t installed automatically, so a newer Wi-Fi or Ethernet driver can wait there for months. To find it:

    1. Press Win + I to open Settings and select Windows Update.
    2. Click Check for updates and install anything pending. Restart if asked.
    3. Go to Advanced options and make sure Receive updates for other Microsoft products is On.
    4. Under Additional options, select Optional updates.
    5. Expand Driver updates. Look for entries with your adapter vendor’s name, such as “Intel – Net” or “Realtek – Network.”
    6. Tick only the network driver and click Download & install.
    7. Restart the PC, even if Windows doesn’t ask.

    Select only the driver you need. Ticking every optional entry at once makes it hard to know which one caused a new problem, and some listings are older than what you already have. Compare the version shown in the listing with the baseline you recorded; if it’s lower, skip it.

    When you update network drivers in Windows 11 this way, the package has passed Microsoft’s driver validation for your hardware ID, which is why this route is the low-risk first choice.

    Find Optional Driver Updates in Windows 10

    Windows 10 hides optional drivers one level deeper:

    1. Open Settings with Win + I.
    2. Select Update & Security, then Windows Update.
    3. Click Check for updates and let pending Windows updates finish.
    4. Click View optional updates below the update status. This link only appears when optional items exist.
    5. Expand Driver updates, tick the network driver, and click Download and install.
    6. Restart the PC.

    If View optional updates never appears, Windows has no newer driver for your hardware in its catalog. That’s common for older laptops and for adapters whose vendors publish updates only on their own sites. Move to the manufacturer route instead of waiting.

    How Do You Update a Driver in Device Manager?

    Device Manager updates a network driver two ways: an automatic search, or a manual install of a package you’ve already downloaded. The manual option is the one that solves most stubborn cases, because current versions of Windows search mainly local and Windows Update sources.

    Search for a Compatible Driver

    1. Right-click Start and select Device Manager.
    2. Expand Network adapters.
    3. Right-click your Wi-Fi or Ethernet adapter and choose Update driver.
    4. Select Search automatically for drivers.

    If Windows finds something newer, it installs it and shows the new version. More often you’ll see “The best drivers for your device are already installed.” That message only means nothing newer exists in the sources Windows checked. It says nothing about the manufacturer’s site.

    From that same window, Windows also offers a link to search for updated drivers on Windows Update, which sends you back to the optional updates page covered above.

    Install a Driver You Have Already Downloaded

    This is the method to use with a manufacturer package, especially when the vendor ships a ZIP of .inf files and no installer:

    1. Extract the download to a simple folder such as C:DriversWiFi.
    2. In Device Manager, right-click the adapter and choose Update driver.
    3. Select Browse my computer for drivers.
    4. Click Browse, pick the extracted folder, and tick Include subfolders.
    5. Click Next and let Windows install the matching .inf.
    6. Restart, then recheck the version on the Driver tab.

    If the vendor’s file is a self-extracting .exe and you want manual control, Intel’s documentation shows how to extract the files from the installation EXE with zip software and then point Device Manager at the folder, checking Include subfolders so it scans the entire driver set.

    Should Windows report the driver isn’t compatible, try Let me pick from a list of available drivers on my computer at step 3 and click Have Disk. That lets you target the .inf directly, and it fails loudly if you downloaded the package for the wrong chipset, which is useful information in itself.

    How Do You Get the Right Driver from the Manufacturer?

    The right driver comes from either your PC maker’s support page for your exact model or the chipset vendor (Intel, Realtek, Qualcomm, MediaTek) for your exact adapter. Getting it wrong usually means a failed install or an adapter that loses vendor-specific power and roaming tuning.

    Match the Download to Your PC, Adapter, and Windows Version

    Check three things before you click download:

    • Model: use the System Model from msinfo32 on the PC maker’s site, or the adapter name from Device Manager on the chipset vendor’s site.
    • Windows version: pick Windows 11 or Windows 10 packages specifically. Ethernet drivers for Windows 10 often install on 11, but Wi-Fi 6 and 6E drivers have version-specific features.
    • Architecture: almost every current PC is 64-bit (x64). ARM laptops need ARM64 drivers.

    Device Manager’s Details tab, with Hardware Ids selected, shows a string like PCIVEN_8086&DEV_A0F0. VEN_8086 is Intel and VEN_10EC is Realtek. When a device name is generic, that ID tells you who made the chip.

    The PC maker’s driver is sometimes older than the chipset vendor’s but tuned for your board’s antennas and power settings. On a laptop, try the PC maker’s version first. On a desktop with an add-in card, go to the card or chipset vendor.

    Use Official Manufacturer Tools When Appropriate

    Most major brands ship update utilities that detect your hardware and pull matched drivers:

    Brand Official tool
    Intel adapters Intel Driver & Support Assistant
    Dell Dell Update / SupportAssist
    HP HP Support Assistant
    Lenovo Lenovo System Update / Vantage
    ASUS MyASUS

    Intel Driver & Support Assistant is particularly handy for Intel Wi-Fi 6 and 6E cards, since Intel often posts new wireless builds there before they reach Windows Update.

    Skip third-party driver update software that promises to fix everything at once. Those tools mix packages from unclear origins, and Microsoft’s own guidance warns against downloading drivers from any websites other than the manufacturer’s official site.

    Install a Driver Offline Using a USB Drive

    When the PC has no working connection at all, use a second computer:

    1. On the dead PC, note the System Model and adapter Hardware ID.
    2. On a working computer, download the matching driver from the manufacturer.
    3. Copy the file to a USB drive.
    4. Plug the drive into the dead PC and copy the file to the desktop.
    5. Run it if it’s an .exe. If it’s a ZIP of .inf files, extract it and use Browse my computer for drivers in Device Manager.

    A practical habit: download your laptop’s current Wi-Fi and Ethernet drivers to a USB stick now, while things work. It turns a no-internet emergency into a five-minute fix.

    How Can You Tell Whether the Update Fixed the Connection?

    You can tell the update worked when the new version shows on the Driver tab and your original symptom no longer reproduces under the same conditions. If it still drops or crawls, measurement tells you whether to look past the PC or reverse the change.

    Confirm the Driver Version and Test Wi-Fi or Ethernet

    Reopen the adapter’s Driver tab and compare the version with your baseline. If the number didn’t change, the install didn’t take, and nothing else you test means much yet.

    Then reproduce the conditions that caused trouble: wake from sleep, move to the far room, start a video call. For slow internet speeds, run a speed test on the same spot and band as before, and check WiFi speed against a wired result. A big gap between wired and wireless points at the radio link; both slow points upstream.

    On Wi-Fi, netsh wlan show interfaces shows signal percentage, receive and transmit rates, and the radio type (802.11ax for Wi-Fi 6). A Wi-Fi 6 adapter that reports 802.11ac after the update has fallen back to an older mode.

    Use Ping, Traceroute, and DNS Checks to Narrow Down the Fault

    A driver only governs your PC’s link to the router, so test in layers:

    • Ping your router (ping 192.168.1.1 or your gateway address). Loss or spikes here are local: driver, signal, or interference.
    • Ping a public host with a ping test. Clean local pings but lossy external ones point at your ISP.
    • Trace the path with tracert. Knowing how to trace a route shows which hop introduces delay.
    • Check jitter for calls and gaming with a network jitter test.
    • Check name resolution. If IPs respond but sites don’t load, troubleshoot DNS issues before blaming hardware.

    PacketTools runs these tools in your browser with no sign-in, and no IPs, queries, or test data are logged or stored.

    Roll Back or Reinstall a Driver That Made Things Worse

    If the new driver made things worse, open the adapter’s Properties, go to the Driver tab, and click Roll Back Driver. You need administrator rights, Windows asks for a reason, and a restart completes it. A grayed-out button means no previous version is stored, which is where your restore point comes in.

    For a corrupted install, use Uninstall device:

    1. In Device Manager, right-click the adapter and choose Uninstall device.
    2. Tick Attempt to remove the driver for this device only if you have a replacement ready, such as on a USB drive.
    3. Restart. Windows reinstalls a driver automatically on boot.

    When problems began right after a Windows update, Microsoft’s troubleshooting guide recommends that you compare the current driver and firmware versions with the versions recommended by the manufacturer before changing anything else.

    Choose a Trusted Driver, Then Verify the Fix

    Start by identifying the exact Wi-Fi or Ethernet adapter in Device Manager, record its driver version, and create a restore point. Check Windows Update’s optional drivers first, since those packages are validated for your hardware. When nothing newer appears there, take the driver from your PC maker or chipset vendor and install it through Browse my computer for drivers, using a USB drive if the PC is offline.

    After installing, confirm the version changed, then ping your gateway, ping an outside host, and run a traceroute to see where any remaining delay lives. If the new driver performs worse, Roll Back Driver returns you to your baseline in under a minute.